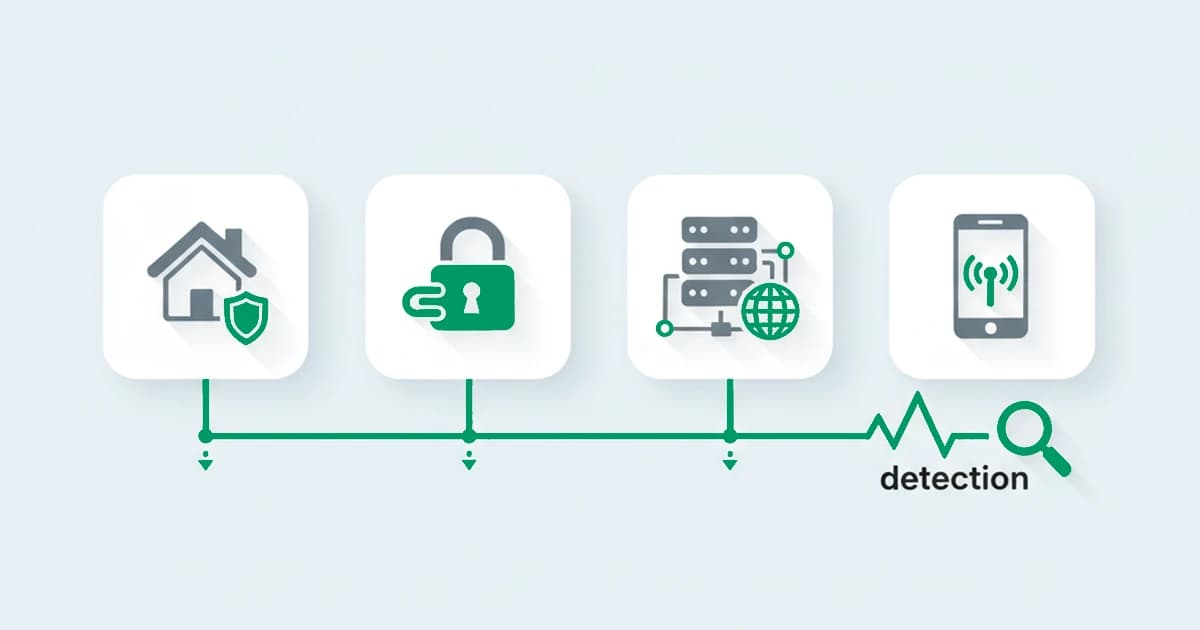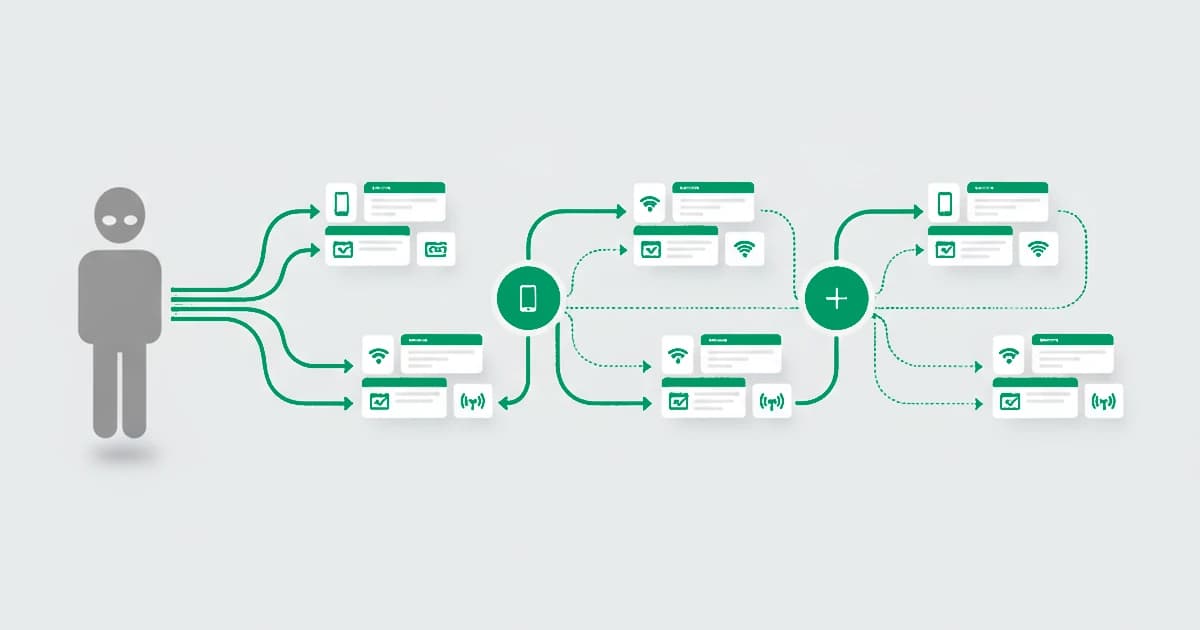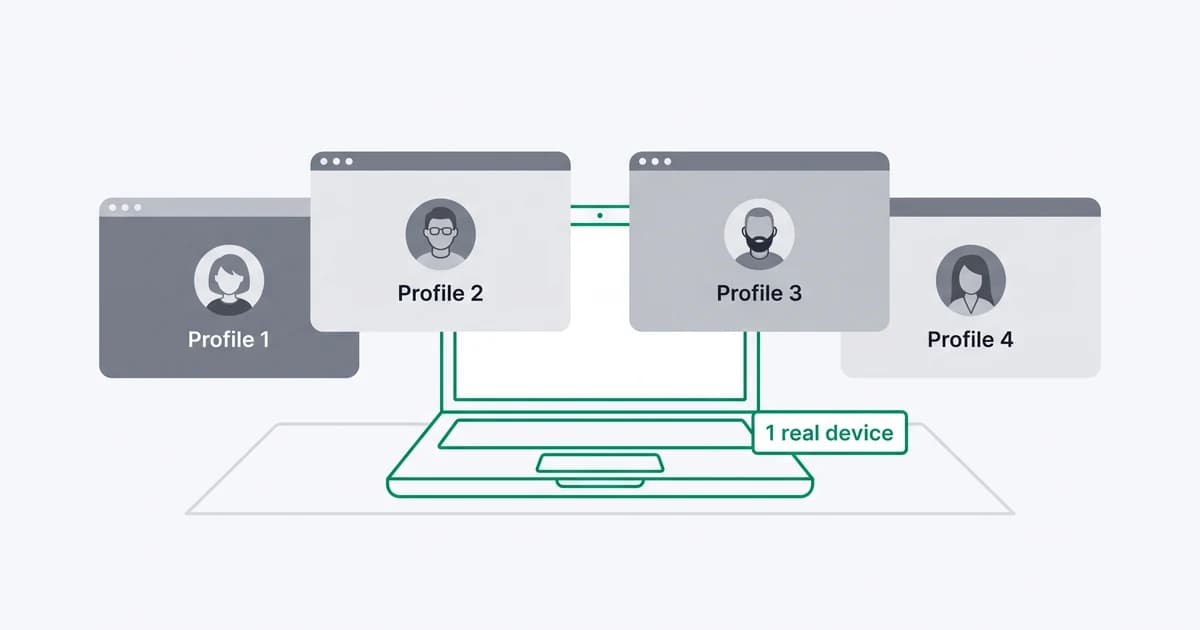
Device Spoofing Detection: Map Techniques to Play Integrity, JA3, JA4
A practitioner checklist mapping anti detect browsers, brokered attestations, and cookie handoffs to Play Integrity, JA3/JA4, and RQ4 signals, with...
Detection methodology, anonymity research, and abuse-prevention playbooks for teams that protect their traffic.

A practitioner checklist mapping anti detect browsers, brokered attestations, and cookie handoffs to Play Integrity, JA3/JA4, and RQ4 signals, with...

For developers: why client probes break after Chrome 76, what detectIncognito.js detects, and when server side signals prove reliable.

Code ready Laravel bot detection: per-endpoint RateLimiter examples, Redis throttling notes, fingerprint signals, honeypots, and guidance on when to use a...
Estimate fraud detection costs with a buyer-focused pricing workbook and worked examples. Validate your projection using ShieldLabs' 5,000 free...
Operational guide for fraud teams on GDPR-compliant device fingerprinting: legal tests, explainable signal scoring, drift handling, and cross-border rules.
Practical, implementation-first guidance for fraud and security teams. Map JA3/JA4, client hints, WebGL and behavioral signals to endpoints, and trigger...
Build an evidence-first defense for marketplace Sybil attacks: payment-weighted reputation, graph-based detection, device and anonymity signals, plus...
A practical ecommerce bot detection playbook: research-backed behavioral models, OWASP-aligned layered defenses, shadow-mode rollout, and explainable risk...
How to stop multi-accounting in online gambling: why players open multiple betting accounts, the signals that link them to one person, and an operator playbook.

How to detect betting bots: the five kinds operators face, the device, network, and timing signals that expose them, and how to stop bot-driven abuse.

HTTP/2 aware header fingerprinting for defenders. Use SETTINGS, WINDOW_UPDATE and pseudo header order to spot impersonation quickly.

A marketer's playbook to handle cookie deprecation impact: audit tags, deploy server-side events, expand first-party capture, and add auditable visitor ID.

Practical 5-stage playbook for product & engineering teams: combine explainable signals, graph-based scoring, and event holds to stop referral fraud.

Fraud teams: detect multi accounting with device, graph, and behavioral signals. Five minute setup; free tier: 5,000 identifications.

Operational playbook for marketers and fraud analysts: three checks, CTIT, conversion baselines and device fingerprints, to detect click spamming early.

Capture deposit to withdraw events, prioritise persistent visitor IDs and cohort signals, and score bonus claims in real time to stop abuse.

How cookies differ from server-side fingerprinting, why many cookieless claims mislead, and practical steps for developers and fraud teams.

SOC playbook for credential stuffing detection: three SIEM-ready rules, triage and containment steps, and how to stream risk signals into your SIEM.

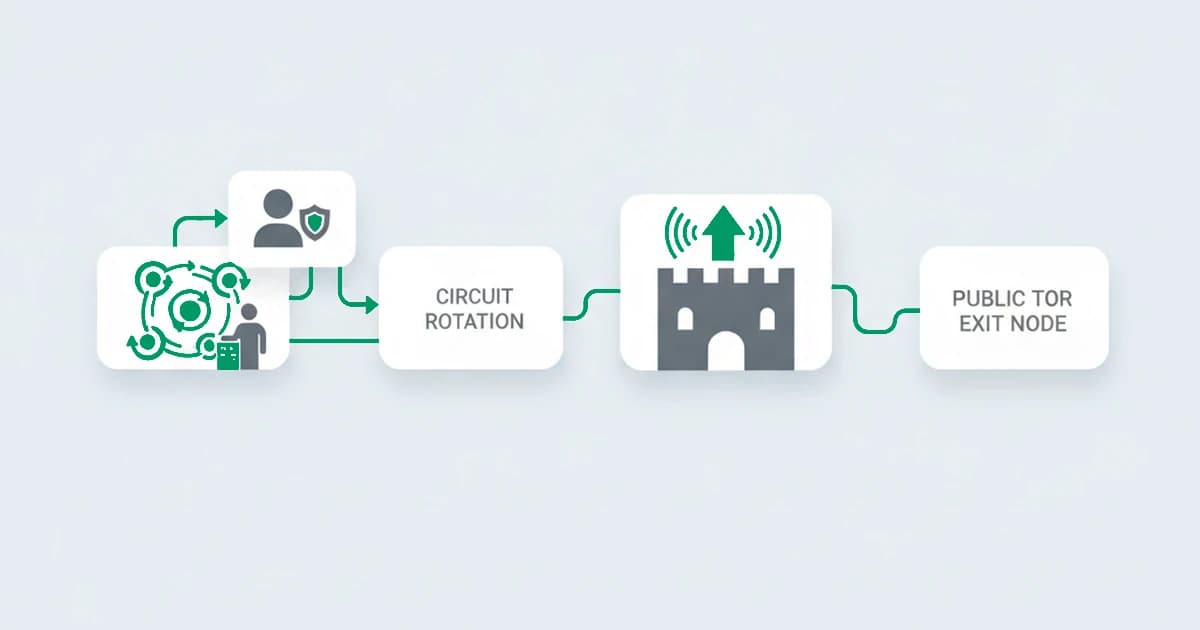
Ops first Tor detection for security engineers: deploy exit lists, DNS/API lookup, TLS fingerprints, and auditable signals in five minutes.

Ops guide to detecting Apple Private Relay. Learn three detection techniques, when to return NXDOMAIN, and fraud safe rules for teams.

Research backed playbook for fraud teams: five low latency checks to spot anti detect browsers, signal to score mapping, and a ShieldLabs setup path.

Detect free trial abuse without blocking real users. Use auditable signals, progressive friction, and metrics to protect conversion.

Cut bot damage on WordPress by detecting early, logging first, and tuning rules safely. Install one JS snippet in about five minutes.

Implement persistent device IDs on Android, iOS, and web: MediaDrm and Keychain storage, migration, privacy best practices, and where ShieldLabs fits.

Practitioner guide to fake signup detection: build a four stage risk funnel and use persistent visitor IDs and auditable signals to cut fake accounts.

Developer-first playbook for Selenium detection across five signal groups: JavaScript flags, CDP artifacts, rendering, network, and behavior.

Implementation focused proxy detection for engineers and fraud teams: APIs, caching, TLS fingerprints, and a 0–100 confidence model to cut false positives.

Dev & Sec teams: detect headless browsers early with JA4/HTTP2 fingerprints, WebGL and CDP timing; includes test-harness practices and risk scoring.

Playbook for fraud teams: measure rule-level false positives, run shadow tests and regression checks, then add visitor ID signals to cut noise.

Operations first playbook to detect card testing: five signals and controls to stop cash out. With ShieldLabs' 5,000 free IDs (one time).

Integration-ready guide for engineering teams adding passive signals to a risk-based auth stack: the four-stage flow and sub-100ms latency targets.

Practical playbook for fraud and product teams deploying visitor identification: prioritized engineering checks, monitoring rules, and vendor evaluation.

Returning visitors convert far better than first-timers, but logged-out shoppers look new. Recognizing the returning device captures the conversion lift.

How to personalize for returning visitors who are not logged in, by recognizing their device with a durable identifier that holds without cookies.

How to keep a returning visitor's cart and preferences across sessions without a login, by recognizing the device with a durable identifier.

Guest checkout removes the account history that flags a repeat fraudster. See how the device behind accountless orders restores that continuity.

A device ban makes a ban stick to the device, not the account, so a banned user cannot walk back in under a fresh email. How it works and how to build it.

What a good new vs returning visitor ratio is, why the cookie-based count in analytics is wrong, and how returning visitors are recognized without cookies.

What ticket scalping is, how scalpers beat per-person limits with fake accounts, and how the device behind those accounts links them back to one buyer.

What referral fraud is, the main types from self-referral to account farming, why it is hard to catch, and how the device behind fake referrals stops it.

What loyalty fraud is, the main types from points theft to fake-account farming, why rewards programs are targets, and how device signals help stop it.

The merchant side of gift card fraud: how fraudsters cash out stolen cards, farm gift-card promos, and how the device behind those accounts links them.

What BNPL fraud is, the main types from account takeover to loan stacking, why the model is so exposed, and how to prevent it with device-level signals.

What a click farm is, how phone farms mass-produce fake installs, signups, and clicks, and how the devices behind that activity cluster back to one operation.

The 8 best bonus and promo abuse prevention tools in 2026, how prevention works by linking many bonus claims back to one person, and how to choose.

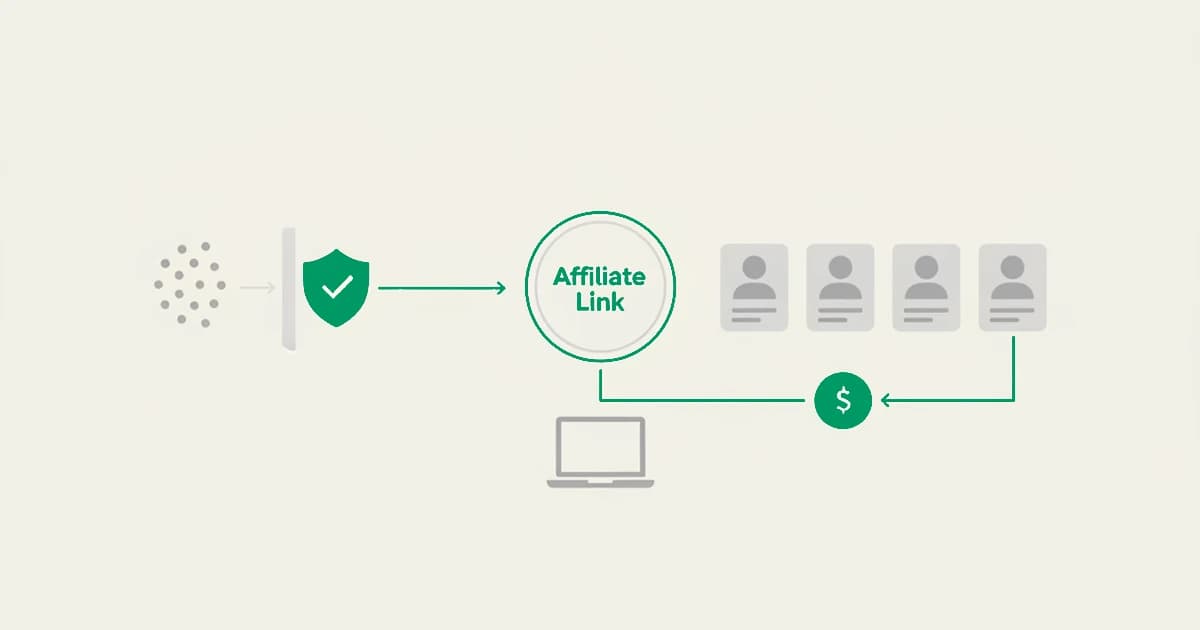
The best affiliate fraud detection tools in 2026, split into click-fraud tools that score traffic in real time and device tools that catch self-referral.

How to prevent bonus abuse in iGaming: the signals that reveal one person behind many accounts, how casinos spot multiple accounts, and how to stop it.

How to detect seat sharing in a SaaS product: spotting one paid seat used by a whole team, the per-seat revenue it leaks, and how to convert sharers.

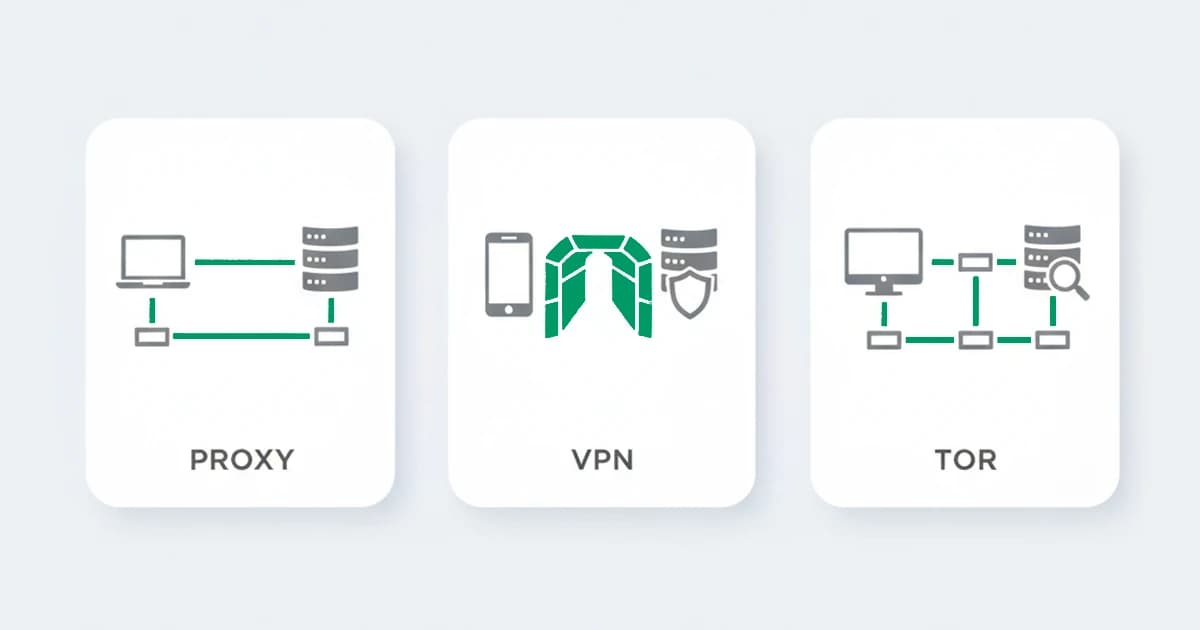
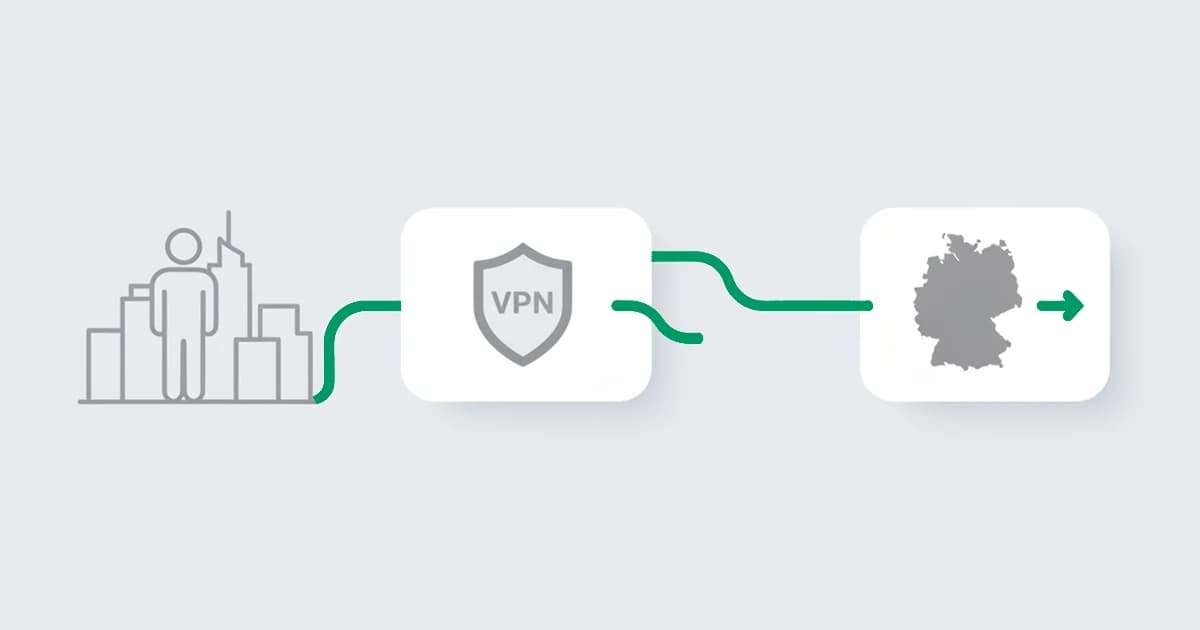
VPN vs proxy vs Tor: how each hides traffic, what each one still reveals, and how a detection layer tells them apart at the network level.

How to prevent gaming fraud: account theft and resale, real money trading farms, cheating and smurfing, and the device signals that link the accounts.

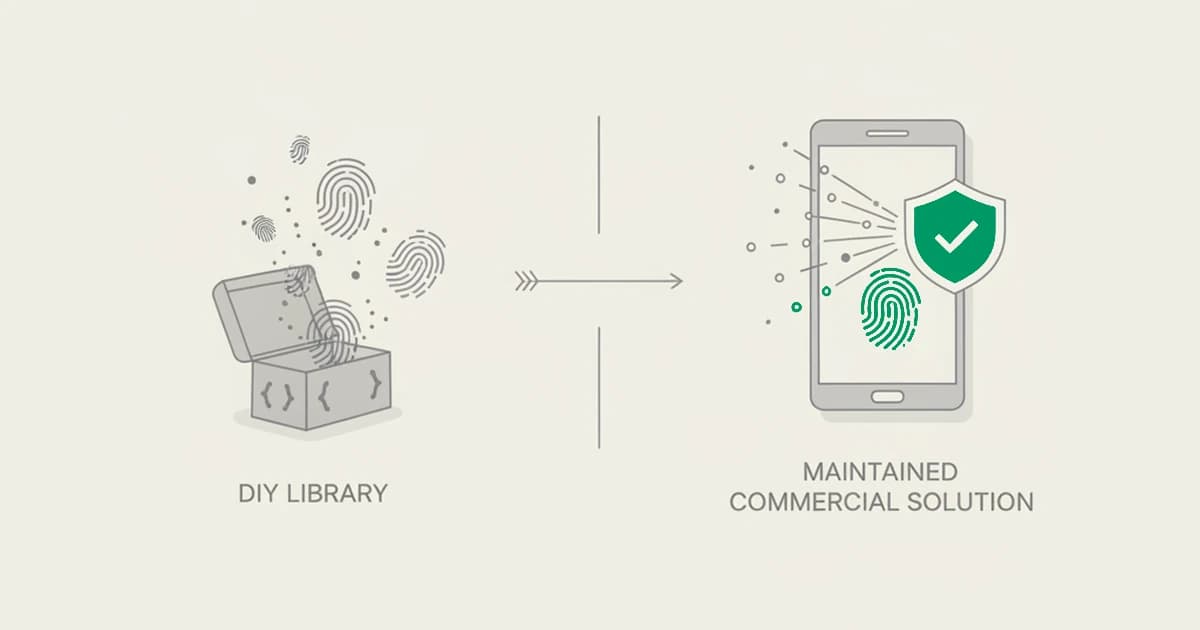
The best device fingerprinting solutions in 2026, split into open-source libraries you self-host and commercial ones that maintain the identifier.

Google retired the Privacy Sandbox in October 2025 and third-party cookies are staying in Chrome. What it was, why it ended, and what it means for fraud.

The main types of marketplace fraud, from triangulation fraud to seller and buyer scams, and how reading the device behind each account links the ring.

The 8 best free-trial abuse prevention tools in 2026, how prevention works by linking many trial signups back to one device, and how to choose.

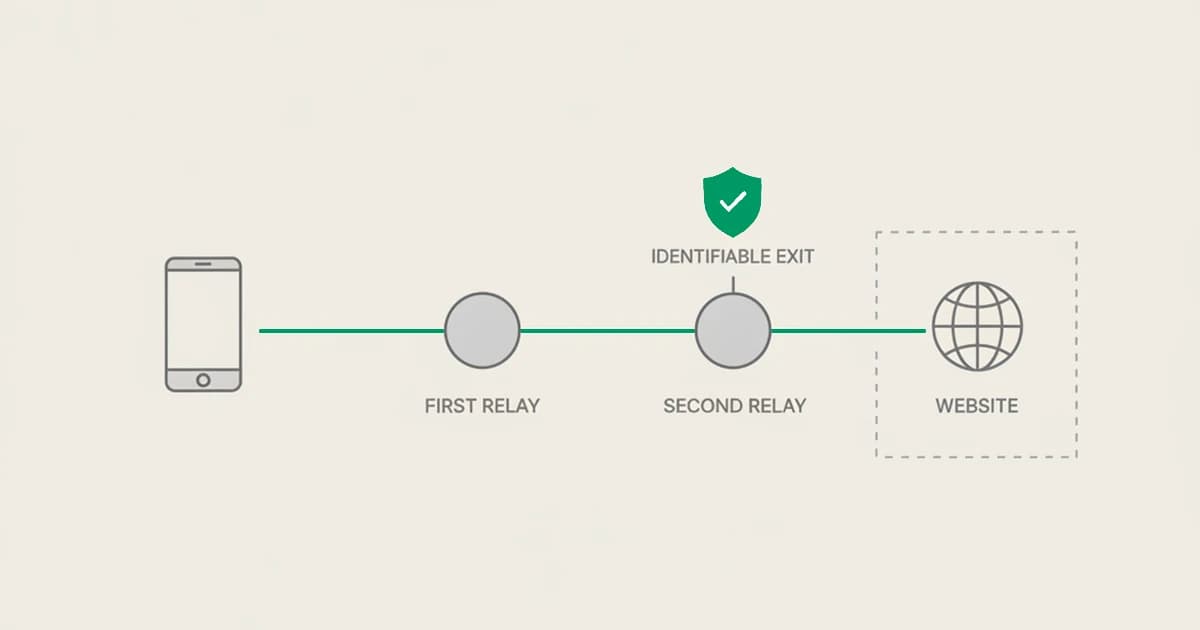
iCloud Private Relay hides a Safari user's IP, but Apple publishes its egress ranges, so it is identifiable. What it is and how to read it for fraud.

How to prevent refund and return abuse: the multi-account refund-ring slice you can detect, how it differs from wardrobing and chargebacks, and how to read it.

What online travel fraud is, the main types from stolen-card bookings to miles theft and fake listings, and how the device behind a booking ties them together.

The fintech fraud types from new-account and synthetic identity to account takeover, payment and BNPL abuse, and mule accounts, and where the device layer fits.

How to prevent coupon abuse: what separates it from coupon fraud and everyday couponing, and how merchants catch one shopper using many accounts.

How to detect invalid traffic (IVT): the GIVT vs SIVT split, what causes it, and the signals advertisers use to catch the traffic draining ad budgets.

The best new-account fraud detection tools for 2026, how signup-fraud detection links many fake accounts back to one device, and how to choose the right layer.

Compare 11 ecommerce fraud prevention tools for small businesses in 2026 by pricing, signal depth, and self-serve fit, plus a framework to choose.

The best anti-detect browser detection tools for fraud teams in 2026, how detection spots spoofed and tampered browser fingerprints, and how to choose.

Why your visitor counts never match across tools. How Google Analytics, Vercel, and ShieldLabs each identify a visitor, and which count is closest to the truth.

How to prevent Sybil attacks: the defenses at the protocol and application layers, and how to catch one actor running many wallets at the frontend.

How to prevent bonus, promo, and coupon abuse: the mechanic behind it, the signals that flag an abused offer, and how to score a claim before you credit it.

What passwordless authentication is, how it works, the main methods from passkeys to magic links, its benefits and limits, and where device signals fit.

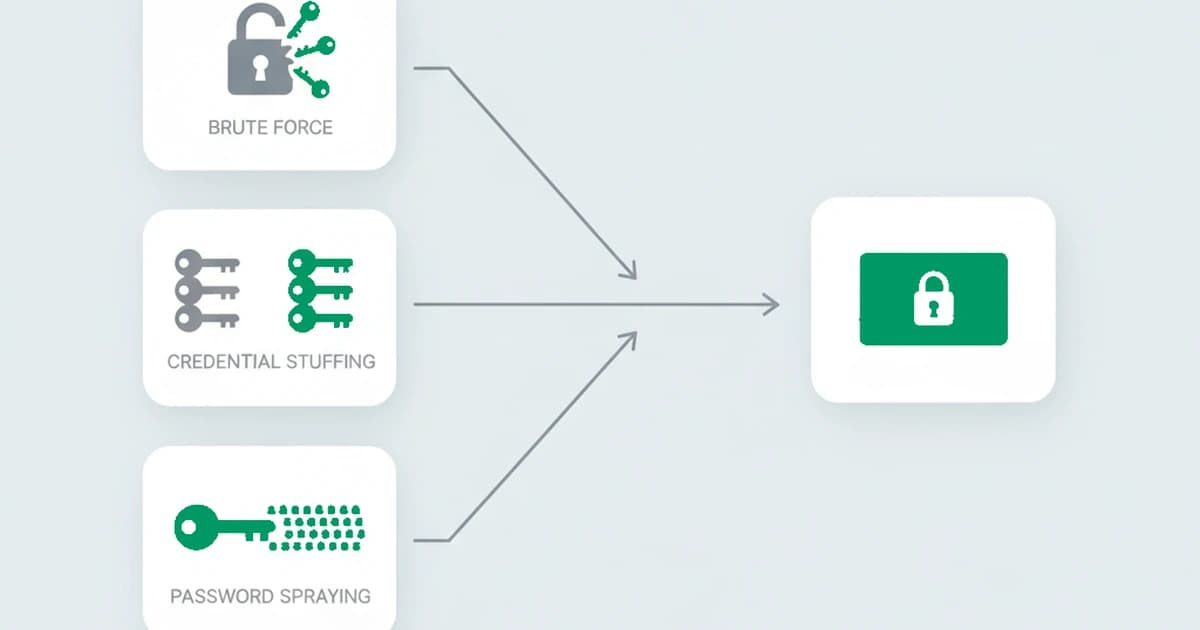
Brute force, credential stuffing, and password spraying all hit your login, but differ in what the attacker knows. The difference, and how to detect each.

Account recovery fraud is how attackers bypass strong login by abusing the reset flow. How it works, why recovery is the weak point, and how to defend it.

What trial farming and credit farming mean on an AI product, not the gaming kind: how one operator drains free compute credits, and where it is caught.

What device-based authentication is, how recognizing a trusted device makes login transparent, how it differs from passkeys and cookies, and where it fits.

How adaptive (risk-based) authentication works, the signals it weighs, and how a recognized device decides when to step up and when to let a user through.

What review fraud is, the main types of fake reviews, why the text alone won't catch them, and how the device behind a review ring gives it away.

Free-trial abuse, API-key abuse, and rate limiting get blamed for each other. Which layer stops what for an AI API, who owns each fix, and where the gap is.

The 7 best CAPTCHA alternatives for 2026, from silent device intelligence to invisible challenges, and how to stop abuse without blocking real users.

How to prevent promo abuse in ecommerce: the tactics behind discount farming, the signals that flag it, and how to score a redemption before you grant it.

How AI companies prevent free-trial abuse: the credit-farming economics, the signals that expose a farmed signup, and how to score it at the API.

A practical guide to the best device intelligence platforms in 2026, how to evaluate them, and which you can evaluate on your own traffic versus sales-led suites.

How payment gateway fraud detection works, layer by layer, what each layer catches and misses, and where reading the device behind the checkout fits in.

How to stop new-account fraud at signup: the abuse-and-evasion kind, why email checks and CAPTCHA miss it, and how to score a registration before it exists.

How to prevent free-trial abuse: what it costs you, the signals that flag a recycled trial, and a playbook to stop it at signup without blocking real users.

What affiliate fraud is, its main types from cookie stuffing to fake leads and self-purchases, and how the device behind a fake conversion gives the ring away.

How to detect ad fraud: the fake clicks, impressions, installs, and leads that drain ad budgets, what each type costs, and the signals that catch them.

How ban evasion detection works: why account-only bans fail, and the signals that re-identify a returning banned user behind a brand-new signup.

The account and offer abuse an ecommerce store faces, why it is not payment fraud, and how to read the device behind each signup without blocking shoppers.

The 10 best multi-accounting detection tools in 2026, how detection works by linking accounts to a shared device and network, and how to choose.

The 14 best account takeover detection tools in 2026, how ATO detection works, and how to choose across device, behavioral, identity, and bot defenses.

What synthetic identity fraud is, how the fabricated-identity lifecycle works, why it is so hard to detect, and how device signals expose the ring behind it.

Card testing fraud sends a burst of small charges to validate stolen cards. The cards rotate, the session does not, and the device behind it is the tell.

The 8 best fraud detection software in 2026, what to look for, and how the options differ across device signals, decisioning, and chargeback protection.

What an IP fraud score means, how Talos, Scamalytics, and IPQS calculate it, why yours can be high through no fault of your own, and what a score misses.

How to detect geolocation spoofing: how it works, why a single IP check fails, and how layered signals expose the mismatch so your team can prevent fraud.

Anti-fingerprint browsers spoof canvas, WebGL, fonts, and TLS to break recognition. How to detect them in 2026, and the tells they leave behind.

What cookieless device identification is, how it recognizes a returning device without a stored cookie, and why it is not the same as cookieless analytics.

What browser spoofing is, what attackers fake (user agent, OS, screen, timezone), and how a spoofed browser betrays itself through signals that disagree.

Compare the best VPN and proxy detection tools for fraud prevention in 2026: what each detects, residential-proxy coverage, pricing, and how to choose.

How to identify anonymous traffic and recognize returning visitors hidden behind VPNs, proxies, Tor, Private Relay, and anti-detect browsers.

Detecting Tor traffic is easy because exit nodes are public. The hard part is acting on it without blocking real users. How web detection actually works.

What iCloud Private Relay and Chrome IP Protection actually change for fraud detection: what degrades, what survives, and why masking is not evasion.

Friendly fraud is when a real customer disputes a purchase they made. How it works, why it is hard to prove, and how device evidence helps you fight it.

WebGL fingerprinting identifies a device by how its GPU renders 3D graphics. How it works, what it reveals, and how it differs from canvas.

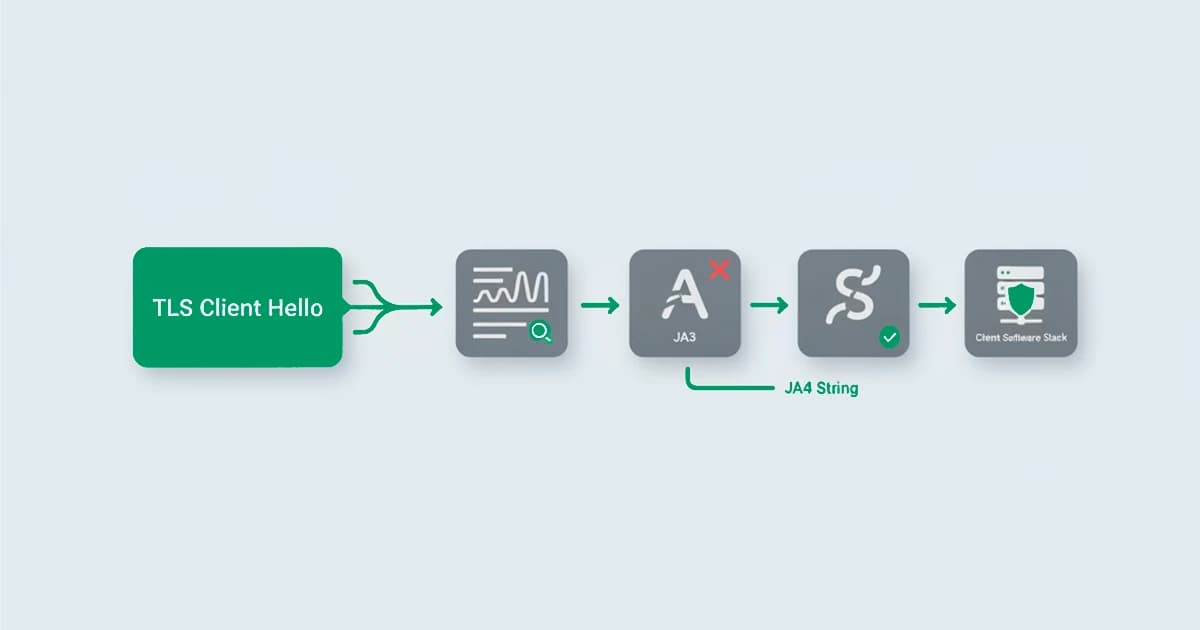
TLS fingerprinting identifies the software behind a connection from its TLS handshake. How it works, what JA3 and JA4 are, and what it reveals.

Font fingerprinting identifies a device by which fonts are installed, read from how text renders. How it works, what it reveals, and how stable it is.

Audio fingerprinting identifies a device by how it processes a sound signal in the browser. How it works, what it reveals, and how stable it is.

How to prevent multi-accounting: detect one person operating many accounts, why IP-based detection fails, and how ready detection stops it.

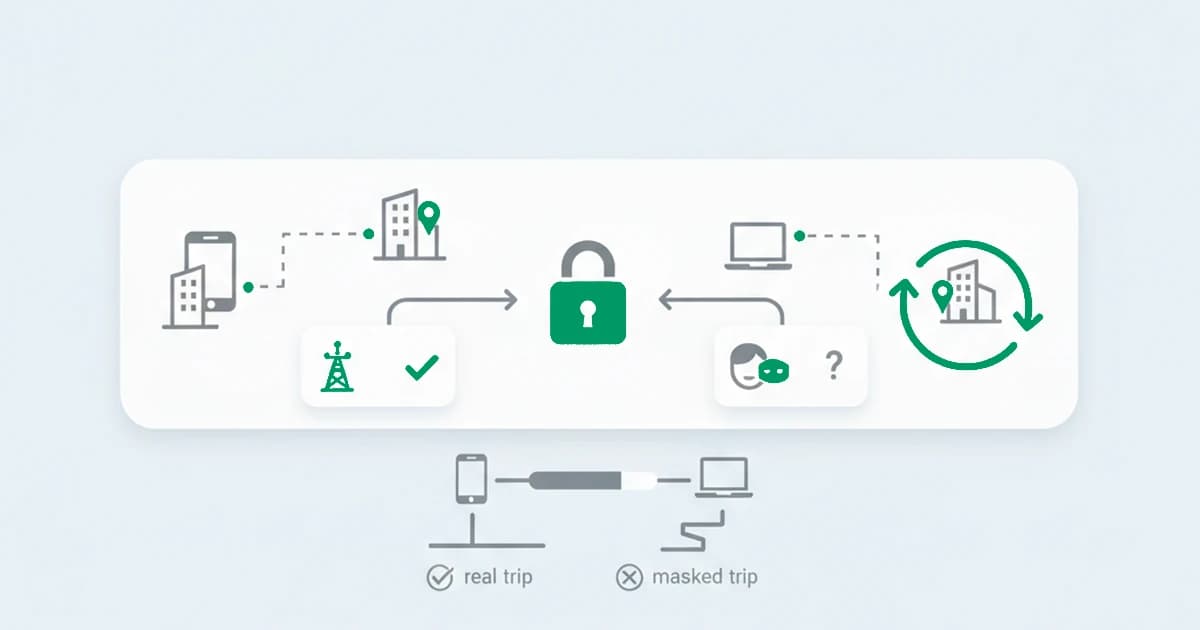
Impossible travel detection flags an account logging in from two far-apart places. Why velocity alone over-fires on VPNs, and how the device fixes it.

How to detect account takeover at login: the device and network signals that flag a suspicious login, why MFA alone misses them, and where the gap is.

WebRTC fingerprinting uses a browser's real-time connection setup to expose network data, including a local or real IP behind a VPN. How it works.

What IP reputation is, how the 0 to 100 score is built, and why a clean IP score alone will not catch fraud. The lagging, shared, and recycled-IP problem.

What JA4 fingerprinting is, how it fixes JA3's weakness to TLS randomization, the JA4 string format and JA4+ suite, and what it can and cannot identify.

How to detect VPNs in 2026: the methods that actually work, why an IP check alone fails, and how masked traffic ties to abuse and risk.

What a residential proxy is, where the home IPs come from, and how residential proxy detection works without relying on the address itself.

What is device fingerprinting: the signals that make up a device fingerprint, how recognition works across browsers, and what teams use it for.

Browser fingerprinting identifies a device from 300+ datapoints. Learn how canvas, WebGL, and IP signals work, plus detection methods and countermeasures.

Canvas fingerprinting identifies a browser by how it renders a hidden image. How it works, what it reveals, how stable it is, and its role in fraud detection.

How account sharing detection works: counting the distinct devices behind one login, the signals that reveal it, and how to act without false positives.

The main browser fingerprinting techniques: canvas, WebGL, audio, fonts, TLS (JA3/JA4), and more, what each one reads and how stable it is.

How proxy detection works for fraud prevention: 13 techniques, why residential proxies are hard to spot, and why an IP check alone is never enough.

Anti-detect browsers fake a new device per profile to power multi-accounting. How to detect them: the signals that expose them and why no one check is enough.