

How to prevent referral fraud

Last updated on July 27, 2026 · 8 min read
Referral programs work because people trust their friends. Nielsen's global trust research has found that 92% of consumers rate recommendations from people they know as the most credible form of advertising, a result it has repeated for over a decade, most recently in 2021. That trust is exactly what makes a refer-a-friend reward cheap growth, and exactly what referral fraud is built to farm.
Referral fraud turns your growth budget into a payout machine for people gaming the rules rather than bringing you real customers. This guide explains what referral fraud is, the main types, why it is so hard to catch, and how to prevent it, including the one signal that gives away a fake referral no matter how distinct the accounts look.
Key takeaways
- Referral fraud is the abuse of a referral program to earn rewards without bringing in genuine new customers, most often through self-referral with fake accounts.
- It is hard to catch because each fake account is built to look like a new, distinct user, with its own email, IP, and details.
- The signal that unmasks it is what the fake accounts share, usually the device behind both the referrer and the accounts they claim to have referred.
- Prevention combines program design, delayed and milestone rewards, verification, with device-level detection that links the referrer to the referred.
What is referral fraud?
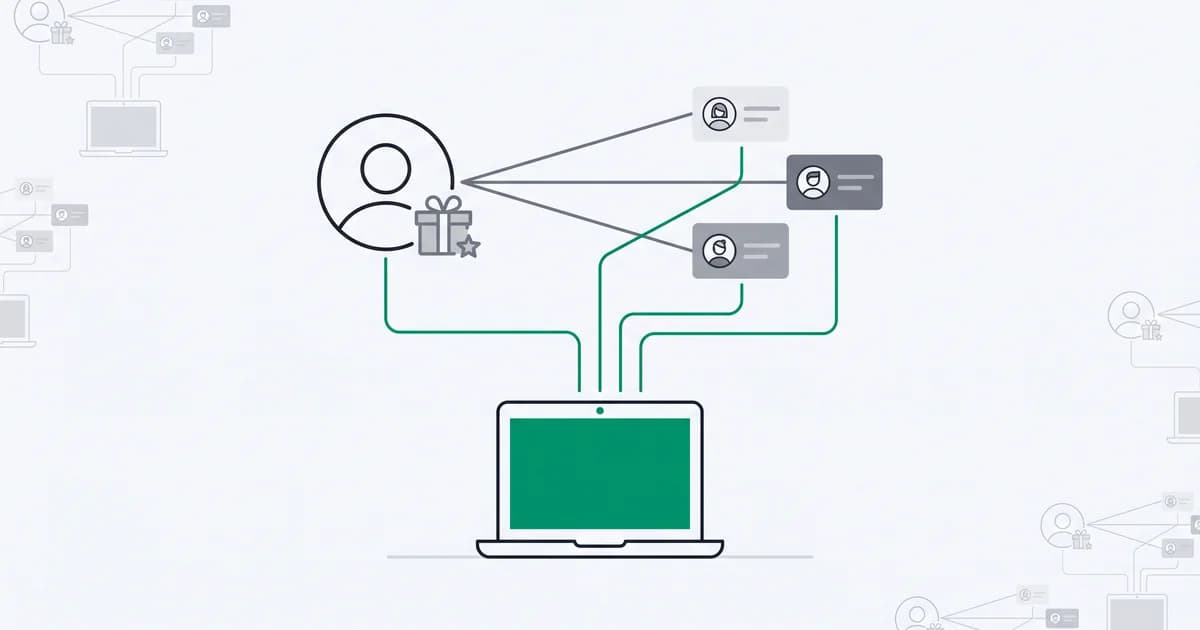
Referral fraud is when someone exploits a referral or refer-a-friend program to collect rewards they did not genuinely earn, typically by referring accounts that are not real new customers. Instead of bringing a real friend to the product, the fraudster manufactures the referral: they create fake accounts, refer themselves through them, and pocket the reward for each one.
It is a first-party abuse, which is what makes it awkward. The person gaming the program is often a real user with a real account who has simply worked out that fake referrals pay. Because the referred accounts each look like an ordinary new signup, the program sees growth and hands out rewards, while the business gets no new customers and a drained incentive budget.
The main types of referral fraud
Referral fraud takes a few recognizable shapes:
- Self-referral. The most common form. One person creates fake accounts and refers themselves through them, collecting the reward for each fake signup. Everything is the same person behind different identities.
- Account farming and cycling. A fraudster mass-produces accounts, or cycles through create-and-delete loops, to claim first-time referral rewards over and over at scale.
- Referral rings and collusion. Groups of people, or one operator running many sock-puppet personas, refer each other in loops so every account both gives and receives rewards.
- Program exploitation. Gaming the rules rather than the identities: stacking a referral bonus with other promos, timing signups around reward windows, or abusing a loophole in how rewards are counted.
- Junk-traffic and affiliate abuse. On the affiliate side, sending low-quality or automated traffic to claim referral or affiliate payouts for signups that never engage.
The through-line for most of these is the same: one actor standing behind many accounts that are supposed to be independent people.
Why referral fraud is hard to catch
Referral fraud hides in the gap between what an account claims to be and what it actually is. Each fake referred account is built to look legitimate: a fresh email, a different name, often a different IP from a VPN or proxy, and a normal-looking signup. Checked one at a time, none of them trips an alarm, because on paper each is just a new user joining through a friend's link.
The rules most programs rely on make it worse. Blocking duplicate emails is trivial to evade with a plus-addressed or disposable inbox, and blocking duplicate IPs both misses a fraudster who rotates connections and punishes real families and offices that share one. The thing all the fake accounts genuinely have in common is harder to fake and easier to miss: the device they were created on. That is the signal that turns a pile of plausible new users back into one person collecting rewards.
The one-actor-many-accounts problem underneath self-referral is measurable at scale. In its 2026 analysis of first-party fraud, Stripe tied 7.4% of signups at AI companies to suspected multi-account abuse, the same mechanic that lets one person stand behind a run of look-alike referrals.
How to prevent referral fraud
No single control stops referral fraud, so prevention layers program design with detection:
- Design the reward to resist farming. Pay out on a milestone the referred user has to reach, a first purchase or sustained activity, rather than on signup alone, so a fake account earns nothing. Delayed and non-monetary rewards cut the payoff further.
- Link the referrer to the referred by device. The strongest single check is whether the referring account and the accounts it referred trace back to one device. A persistent device identifier catches self-referral even when emails and IPs differ.
- Watch velocity and anonymity. A burst of referrals in a short window, or referred accounts arriving over VPNs, proxies, and anti-detect browsers, is a strong ring signal, since real friends do not usually sign up ten at a time behind masked connections.
- Verify the new customer, not just the email. Light identity or payment verification on the referred account, sized to the reward, filters out disposable signups without adding friction for real referrals.
- Review before you pay. Hold high-value or high-velocity referral rewards for a quick check rather than paying instantly, so the obvious rings are caught before the money leaves.
Done together, these keep the program open for real advocates while making manufactured referrals unprofitable.
Preventing referral fraud with ShieldLabs
ShieldLabs gives a referral program the device signal that separates a real advocate from a self-referral ring. You add one JavaScript snippet to your signup and referral flows, and each account returns persistent identification that survives cleared cookies and a rotated IP, so the referring account and the accounts it claims to have referred stay linked even when every email and IP differs. ShieldLabs detects that multi-accounting directly as a High-Risk Event, rather than leaving it for you to reconstruct.
We ran a self-referral pattern through the device layer to see how much held up when the accounts were built to look independent, each carrying its own email, IP, and anti-detect browser profile. Every referred account still linked back to the referrer's device, the Multi-accounting event the identifier surfaces, tying them together with 99.9% identification accuracy. Spoofing the surface is cheap: in 2022, when Chrome began reducing the user-agent string, a rewritten user-agent changed nothing about the device traits underneath that keep repeating.
Alongside it, each visit returns a risk score from 0 to 100 and the named risk signals, VPN, proxy, Tor, and anti-detect browser use, that fraudsters lean on to make one person look like many distinct referrals. ShieldLabs scores the session, names the evidence, and helps block fraudulent referrals. You read the High-Risk Event and the score through the API and webhooks and choose the action for each referral: pay, hold, or reject. The free tier covers your first 5,000 identifications.
Sources
- Nielsen: Global Trust in Advertising and Brand Messages
- Wikipedia: Referral marketing
- Wikipedia: Sock puppet account
- Stripe: Analyzing first-party fraud trends: account, free-trial and refund abuse (2026)
Recommended
Frequently asked questions
- What is referral fraud?
- Referral fraud is the abuse of a referral or refer-a-friend program to earn rewards without bringing in genuine new customers. The most common form is self-referral, where one person creates fake accounts, refers themselves through them, and collects the reward for each. Because each referred account looks like an ordinary new signup, the program pays out while the business gains no real customer.
- Is referral fraud illegal?
- It depends on the scale and intent. Deliberately manufacturing fake accounts to extract rewards you did not earn is a breach of a program's terms and can amount to fraud, though most cases are handled as a terms-of-service violation, with rewards clawed back and accounts banned, rather than as a criminal matter. Organized, large-scale rings that steal significant sums are more likely to draw legal action.
- How do you detect referral fraud?
- By finding what the supposedly independent accounts share rather than what they show. The strongest signal is a shared device linking the referrer to the accounts they referred, followed by network and risk signals like VPN or anti-detect browser use, and behavioral links such as signup velocity or shared payment details. No single check is conclusive, so detection correlates several signals to expose one person behind many referrals.
- How do companies stop self-referral?
- With a mix of program design and detection. Paying rewards only when a referred user reaches a real milestone removes the payoff for fake signups, while device-level detection links a self-referrer to their own fake accounts even when emails and IPs differ. Adding velocity limits and light verification on the referred account closes most of the remaining gaps.
- Does ShieldLabs stop referral fraud?
- Yes. ShieldLabs stops referral fraud at the device layer: it surfaces the device and risk signals behind it and detects Multi-accounting directly as a High-Risk Event, which gives away self-referral, while your referral program stays yours. It links a referrer to the accounts they referred with persistent identification and returns a risk score with the named signals, so your team chooses which rewards to pay or hold. The free tier covers your first 5,000 identifications.
Related articles
Remember This Device for MFA With a Persistent Device ID
Design remember this device for MFA with a revocable trust credential, persistent device context, expiry and step-up authentication for sensitive actions.

How to Detect AI Agents on a Website
Detect AI agents on a website by separating operator identity, automation evidence and authorization. Protect accounts while permitting useful public crawling.

Fraud Detection API for Web Apps: From Browser Signal to Backend Decision
Integrate a fraud detection API into web signup and login with browser collection, verified server results, signed webhooks and clear timeout handling.