

Stop Sybil Attacks Without KYC: Evidence-First Prevention for Marketplaces
Build an evidence-first defense for marketplace Sybil attacks: payment-weighted reputation, graph-based detection, device and anonymity signals, plus...
Blog / Detection
Build an evidence-first defense for marketplace Sybil attacks: payment-weighted reputation, graph-based detection, device and anonymity signals, plus...
How to stop multi-accounting in online gambling: why players open multiple betting accounts, the signals that link them to one person, and an operator playbook.
How to detect betting bots: the five kinds operators face, the device, network, and timing signals that expose them, and how to stop bot-driven abuse.

HTTP/2 aware header fingerprinting for defenders. Use SETTINGS, WINDOW_UPDATE and pseudo header order to spot impersonation quickly.

Practical 5-stage playbook for product & engineering teams: combine explainable signals, graph-based scoring, and event holds to stop referral fraud.
Fraud teams: detect multi accounting with device, graph, and behavioral signals. Five minute setup; free tier: 5,000 identifications.
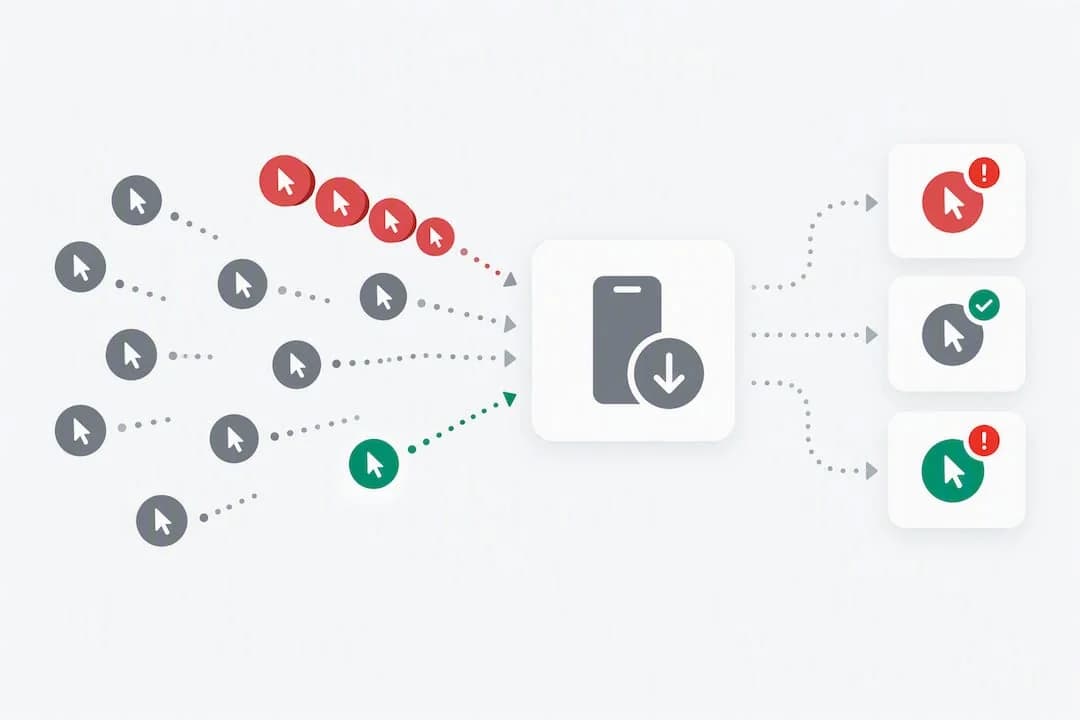
Operational playbook for marketers and fraud analysts: three checks, CTIT, conversion baselines and device fingerprints, to detect click spamming early.
Capture deposit to withdraw events, prioritise persistent visitor IDs and cohort signals, and score bonus claims in real time to stop abuse.
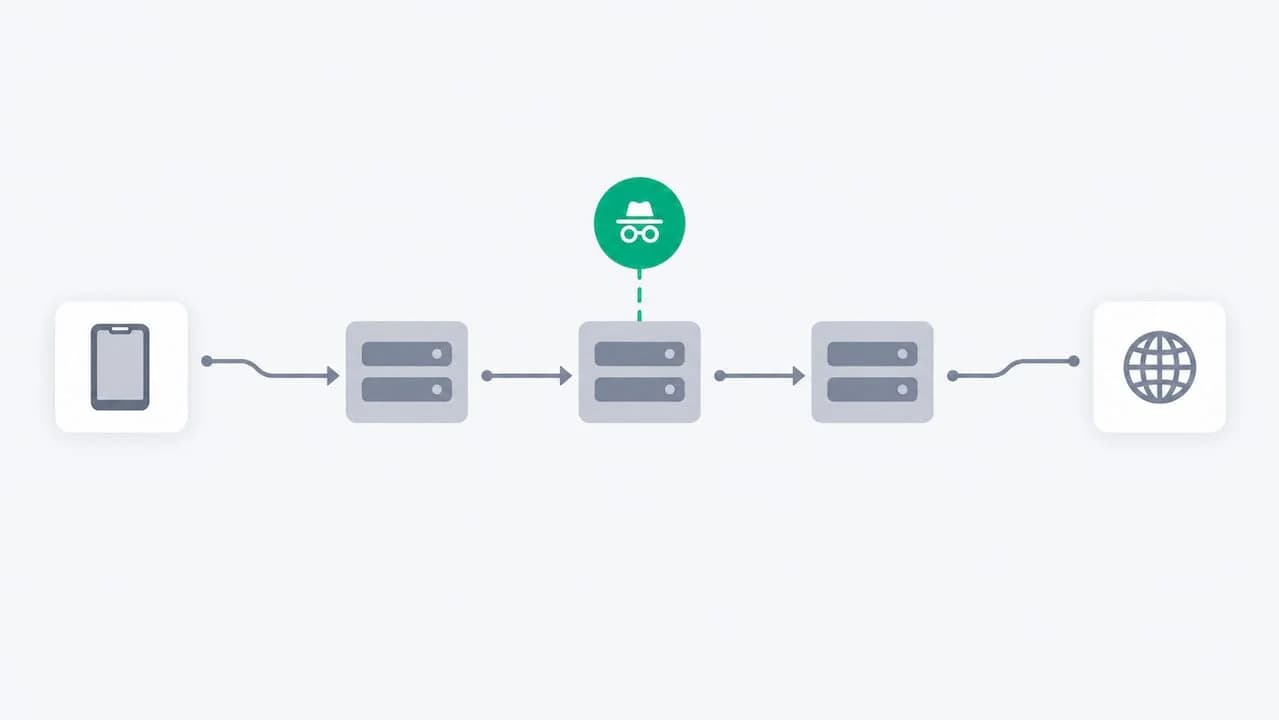
Ops guide to detecting Apple Private Relay. Learn three detection techniques, when to return NXDOMAIN, and fraud safe rules for teams.
Research backed playbook for fraud teams: five low latency checks to spot anti detect browsers, signal to score mapping, and a ShieldLabs setup path.
Detect free trial abuse without blocking real users. Use auditable signals, progressive friction, and metrics to protect conversion.
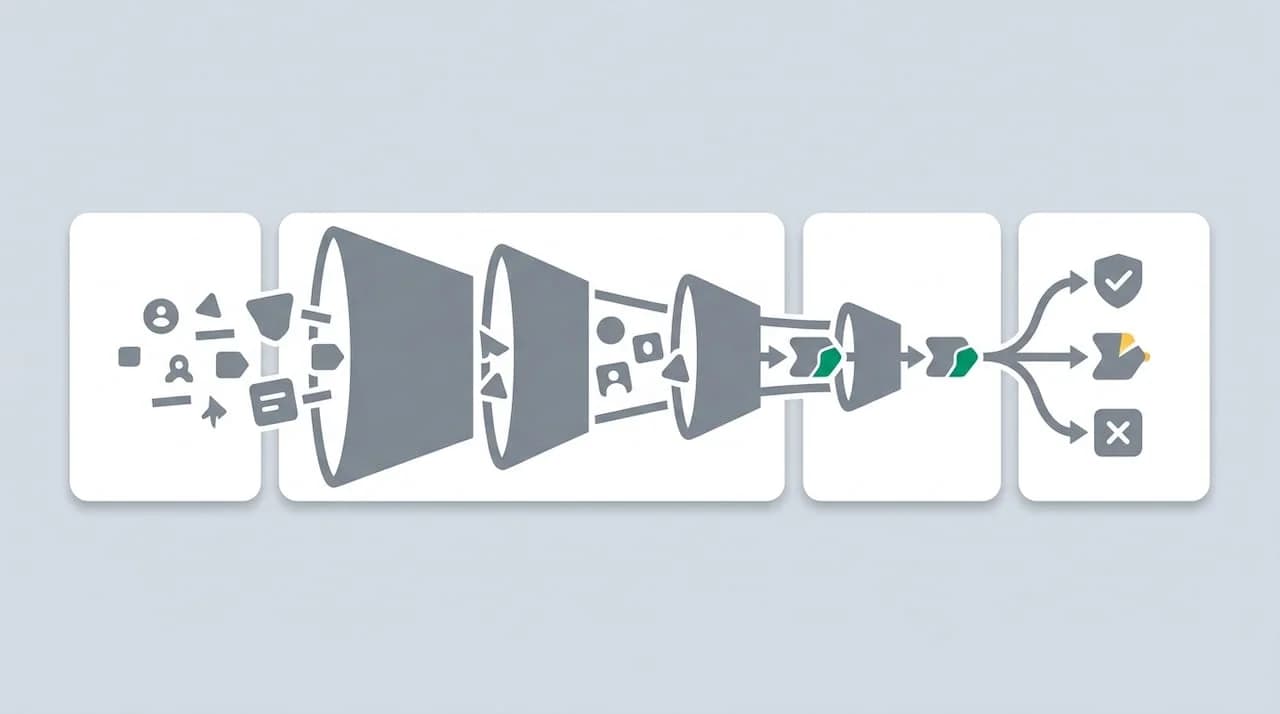
Practitioner guide to fake signup detection: build a four stage risk funnel and use persistent visitor IDs and auditable signals to cut fake accounts.
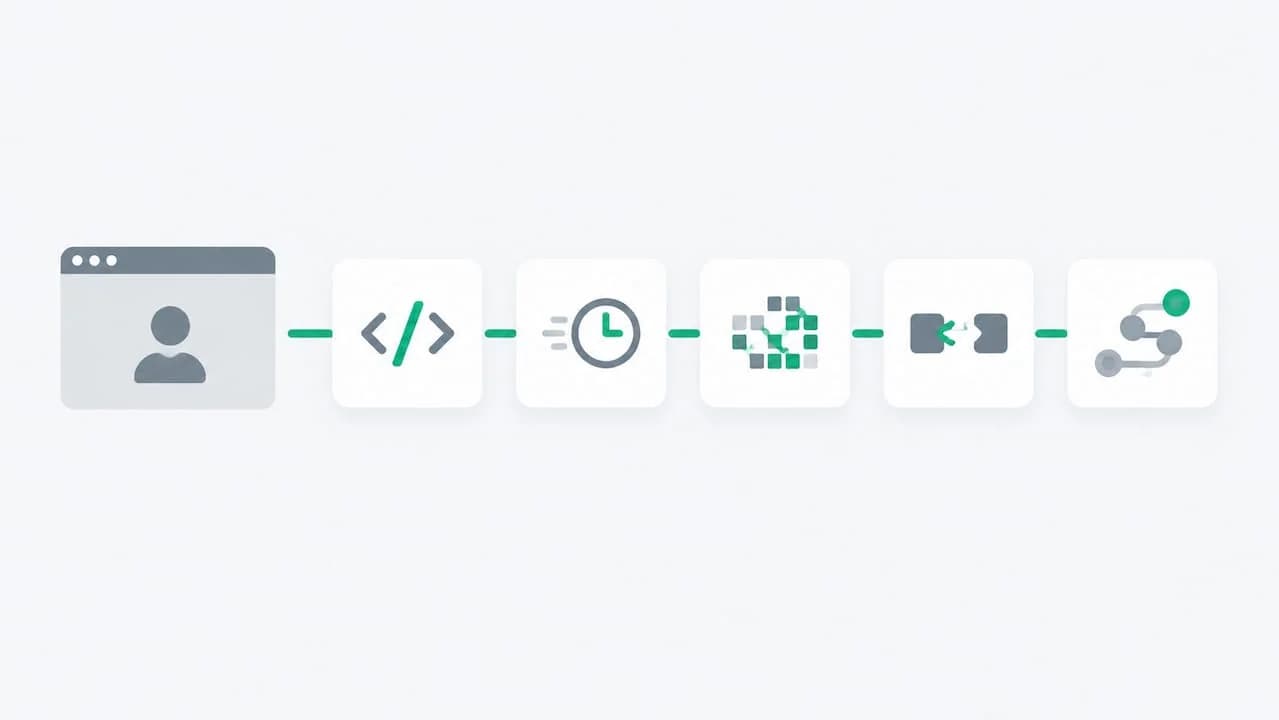
Developer-first playbook for Selenium detection across five signal groups: JavaScript flags, CDP artifacts, rendering, network, and behavior.
Playbook for fraud teams: measure rule-level false positives, run shadow tests and regression checks, then add visitor ID signals to cut noise.
Operations first playbook to detect card testing: five signals and controls to stop cash out. With ShieldLabs' 5,000 free IDs (one time).
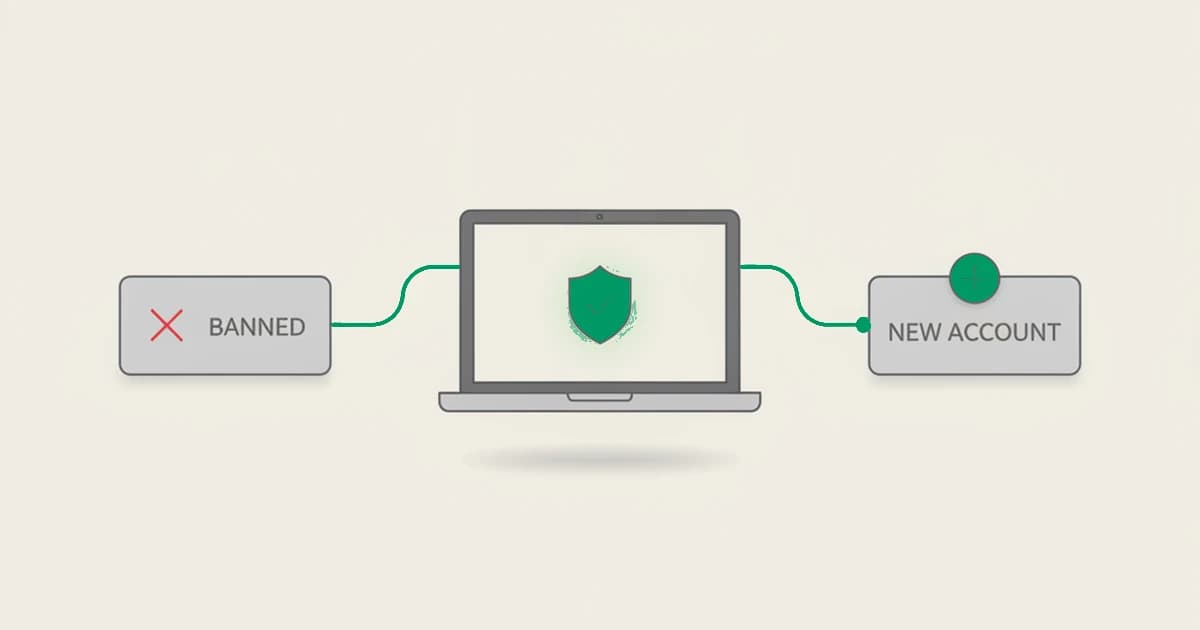
A device ban makes a ban stick to the device, not the account, so a banned user cannot walk back in under a fresh email. How it works and how to build it.
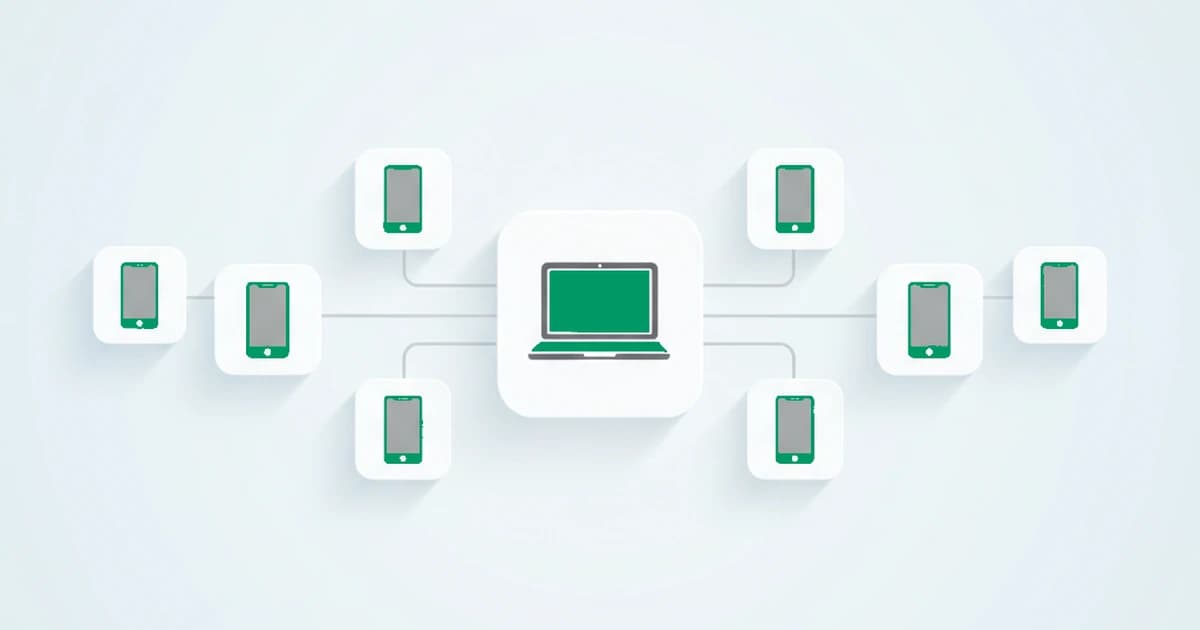
What a click farm is, how phone farms mass-produce fake installs, signups, and clicks, and how the devices behind that activity cluster back to one operation.
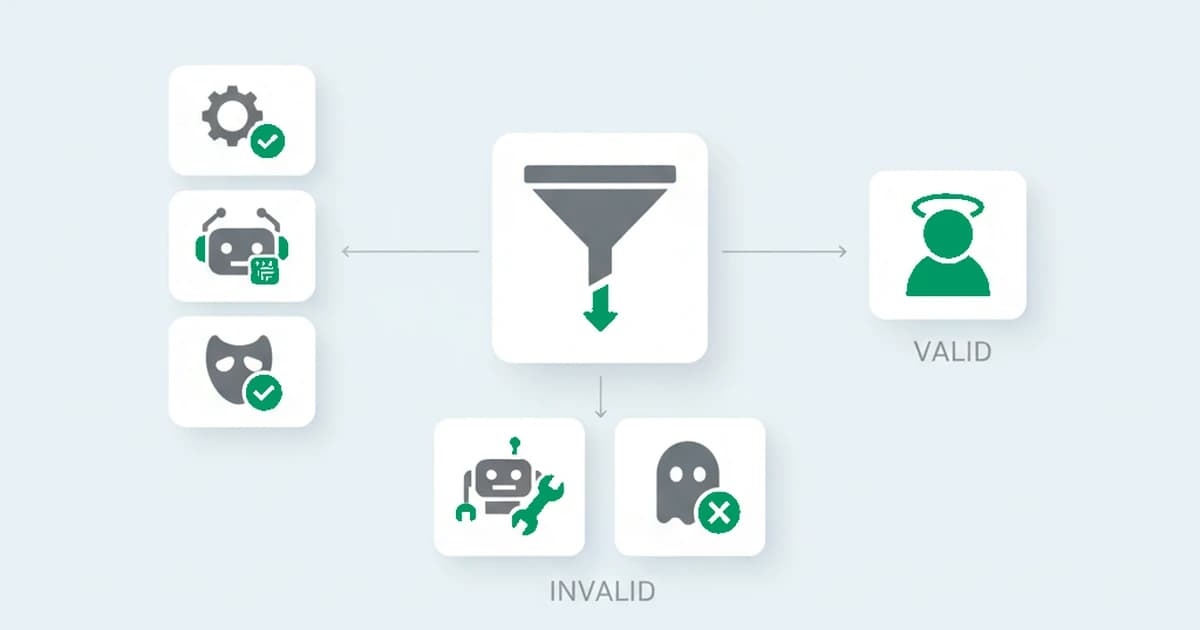
How to detect invalid traffic (IVT): the GIVT vs SIVT split, what causes it, and the signals advertisers use to catch the traffic draining ad budgets.
Account recovery fraud is how attackers bypass strong login by abusing the reset flow. How it works, why recovery is the weak point, and how to defend it.
What review fraud is, the main types of fake reviews, why the text alone won't catch them, and how the device behind a review ring gives it away.
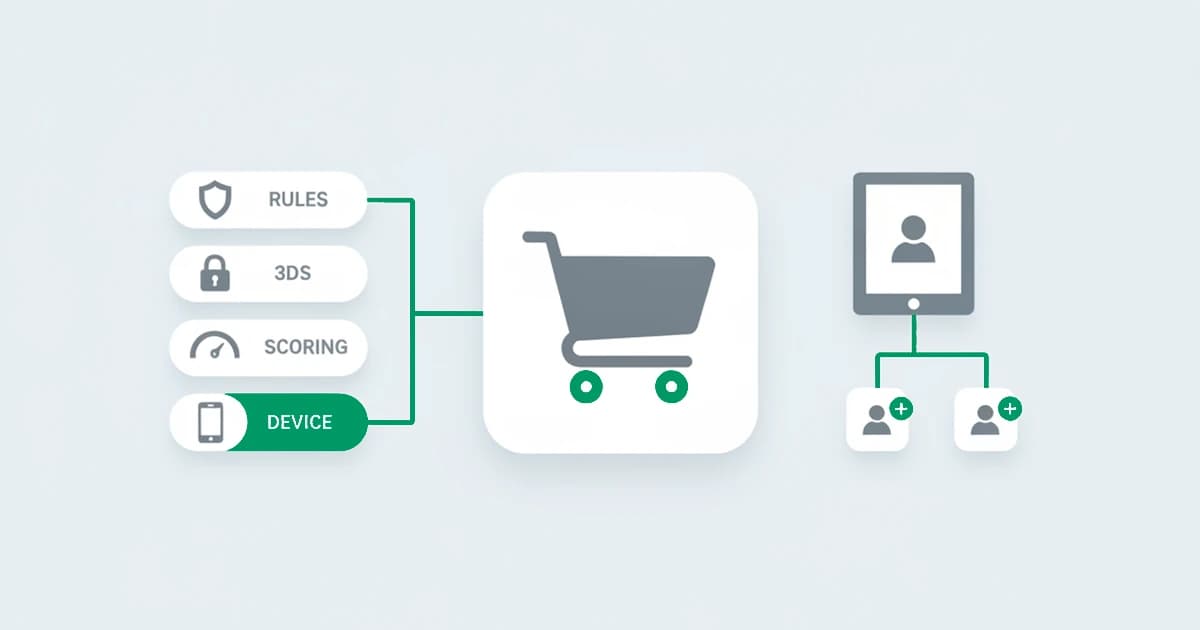
How payment gateway fraud detection works, layer by layer, what each layer catches and misses, and where reading the device behind the checkout fits in.
How to detect ad fraud: the fake clicks, impressions, installs, and leads that drain ad budgets, what each type costs, and the signals that catch them.
How ban evasion detection works: why account-only bans fail, and the signals that re-identify a returning banned user behind a brand-new signup.
How to detect geolocation spoofing: how it works, why a single IP check fails, and how layered signals expose the mismatch so your team can prevent fraud.
Anti-fingerprint browsers spoof canvas, WebGL, fonts, and TLS to break recognition. How to detect them in 2026, and the tells they leave behind.
How to identify anonymous traffic and recognize returning visitors hidden behind VPNs, proxies, Tor, Private Relay, and anti-detect browsers.
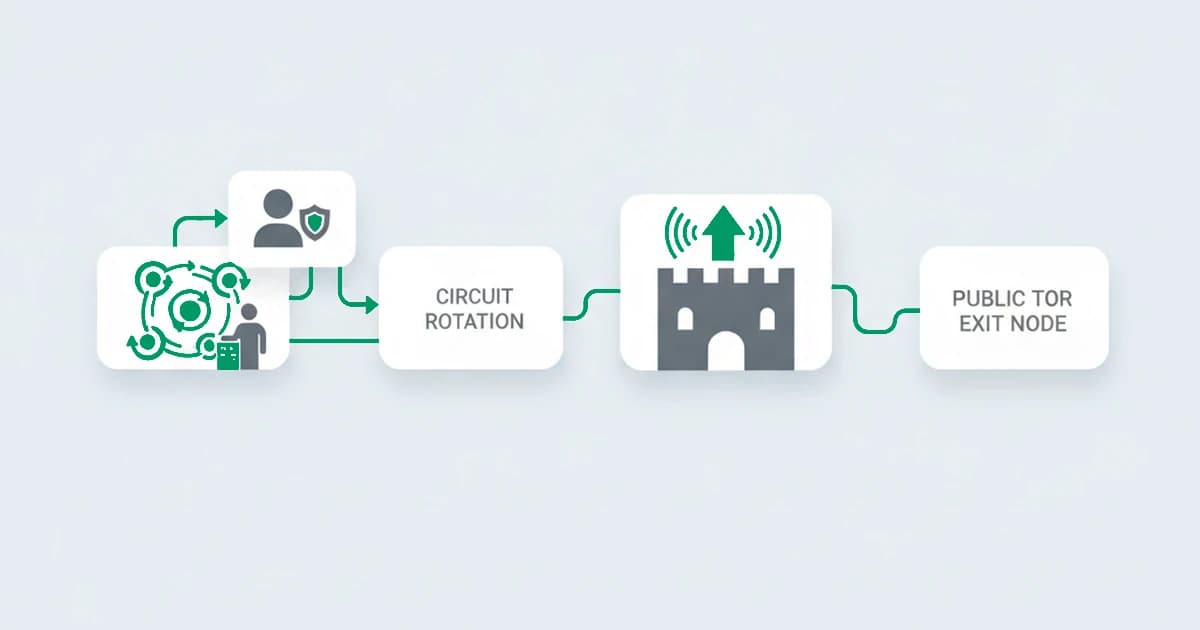
Detecting Tor traffic is easy because exit nodes are public. The hard part is acting on it without blocking real users. How web detection actually works.
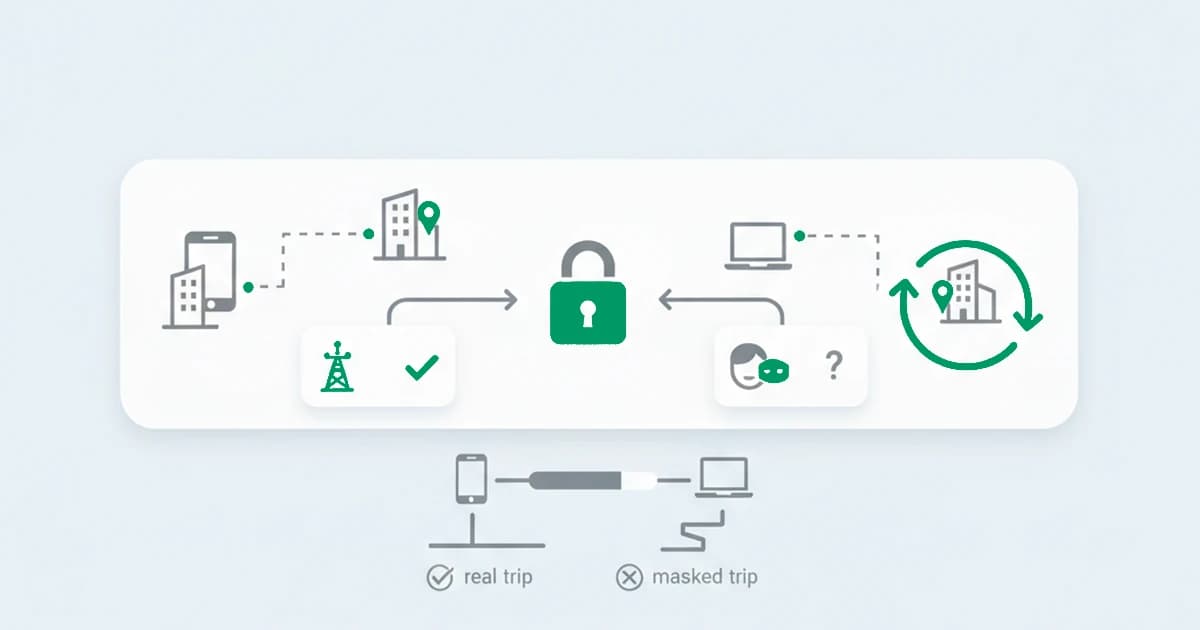
Impossible travel detection flags an account logging in from two far-apart places. Why velocity alone over-fires on VPNs, and how the device fixes it.
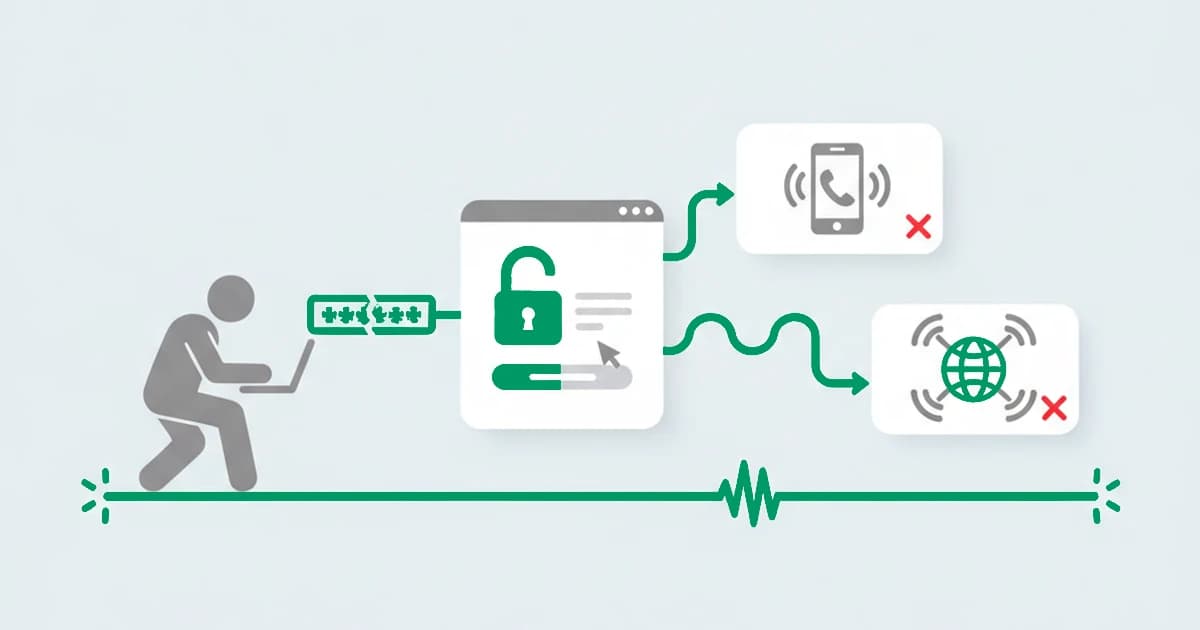
How to detect account takeover at login: the device and network signals that flag a suspicious login, why MFA alone misses them, and where the gap is.
How to detect VPNs in 2026: the methods that actually work, why an IP check alone fails, and how masked traffic ties to abuse and risk.
What a residential proxy is, where the home IPs come from, and how residential proxy detection works without relying on the address itself.
How account sharing detection works: counting the distinct devices behind one login, the signals that reveal it, and how to act without false positives.
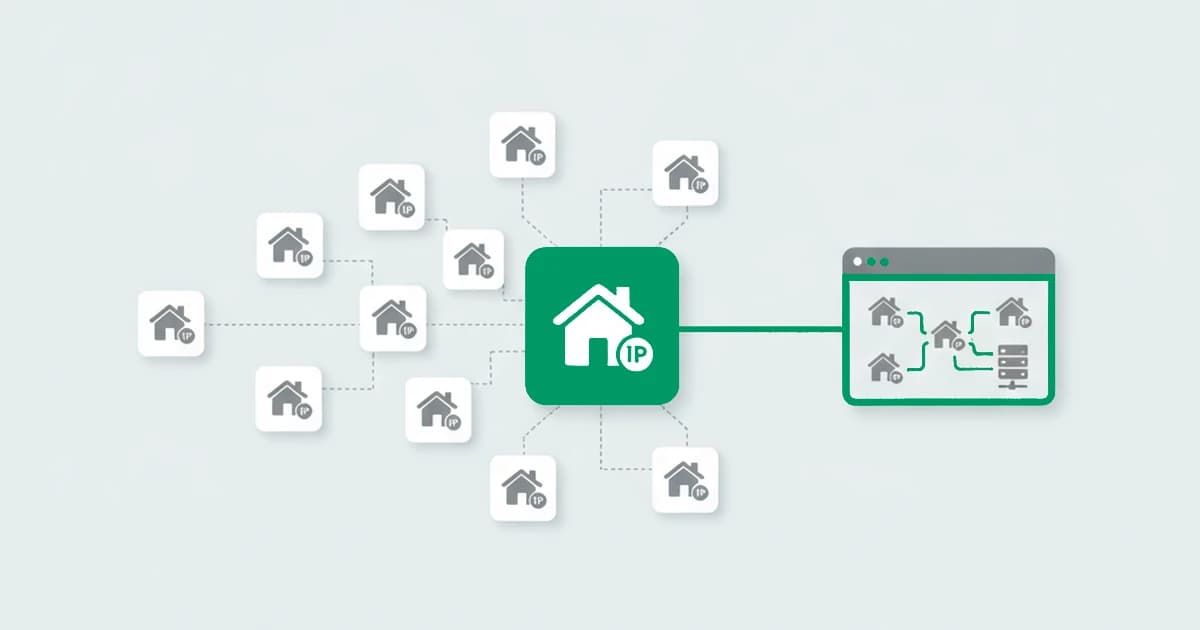
How proxy detection works for fraud prevention: 13 techniques, why residential proxies are hard to spot, and why an IP check alone is never enough.
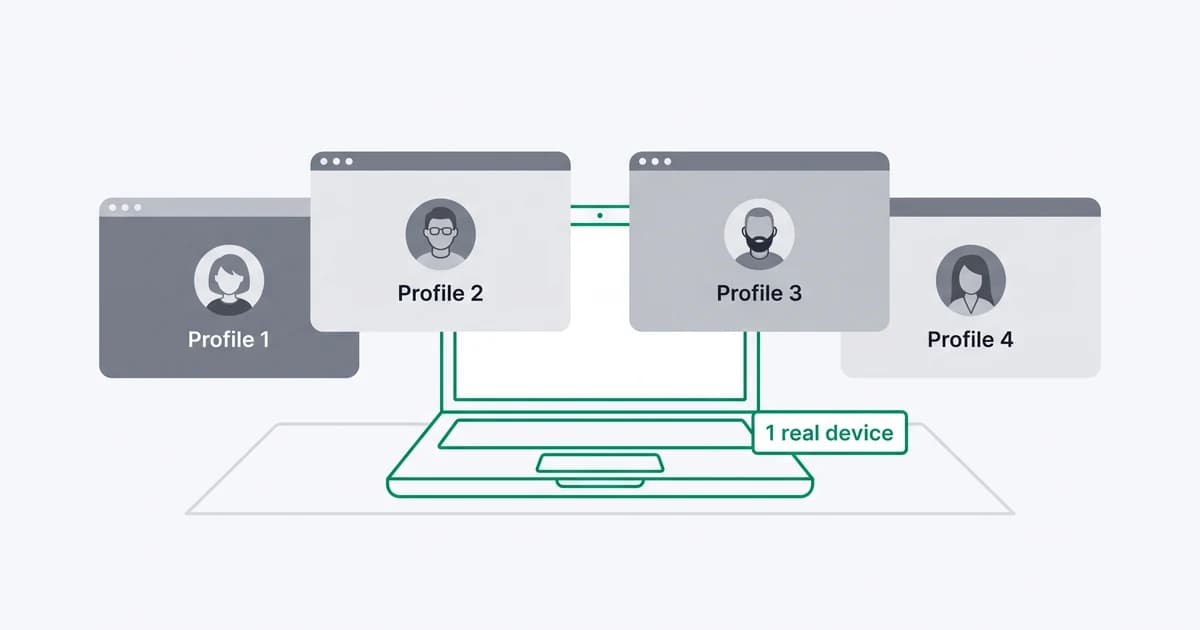
Anti-detect browsers fake a new device per profile to power multi-accounting. How to detect them: the signals that expose them and why no one check is enough.


