

5-Stage Referral Fraud Detection for Product & Engineering Teams

Last updated on October 8, 2026 · 11 min read
The most effective referral fraud detection approach layers device, network, and behavioral signals into a relationship-scoring workflow, then delays reward payout until a qualifying event confirms the referral was genuine. Stripe and Extole both frame this as an operating process, not a single filter, and a tool like ShieldLabs can supply the underlying signals. Graph-based methods may uncover relationships that rules on individual accounts miss, as described in academic research, while EY frames the whole thing as continuous governance rather than a one-time build.
TL;DR:
- Referral programs should set review thresholds from their own traffic and outcomes; a shared IP alone does not prove abuse.
- Device, IP, email, and timing signals should be analyzed together, with risk banding used to trigger verification rather than automatic rejection based on single indicators.
- Combining rules with graph analysis and machine learning improves detection of coordinated fraud patterns, especially in complex referral networks.
- Rewards must remain pending until a confirmed conversion event occurs, with industries establishing specific qualifying milestones like order fulfillment or KYC approval.
- ShieldLabs offers a detection layer that identifies returning visitors and surfaces signals for review, integrating easily through JavaScript or SDK without replacing internal decision workflows.
What Does a Referral Fraud Detection Workflow Look Like?
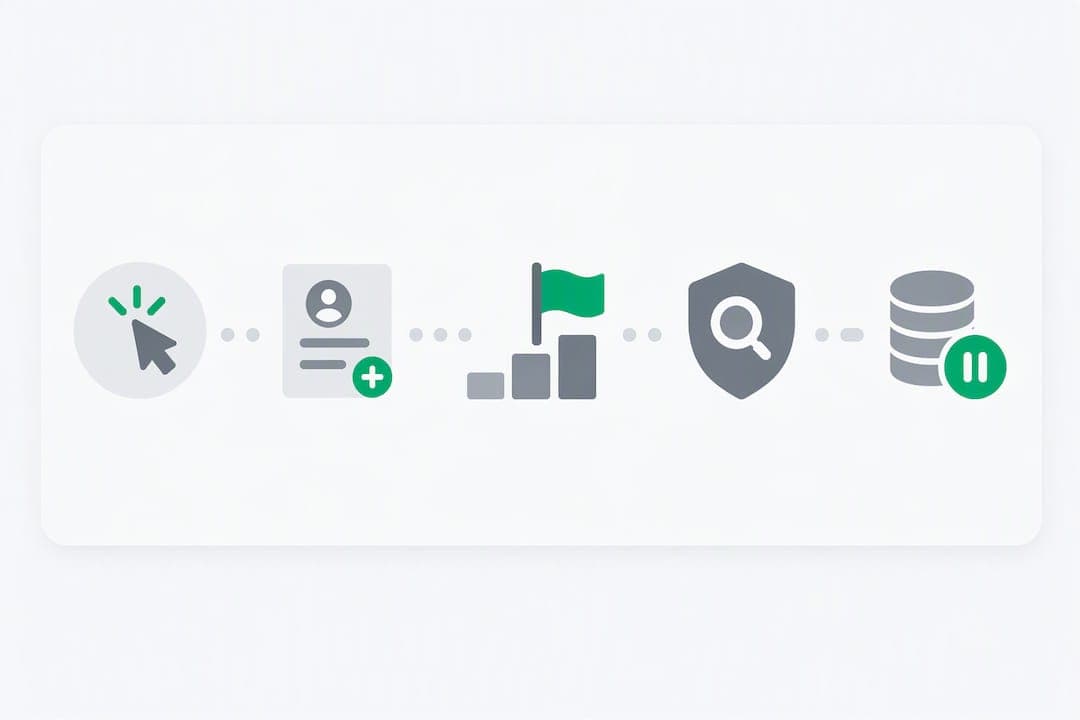
A working referral fraud detection pipeline runs through five stages, each with a distinct owner and a distinct failure mode if skipped.
- Signal collection at click and signup. Capture device fingerprint, IP and network reputation, email metadata, and timing data the moment a referral link is clicked and again at account creation.
- Entity linking. Connect referrer, referee, device, network, and payment identifiers into a single relationship record, not isolated event logs.
- Relationship scoring. Score the connection between referrer and referee, not just the referee's individual risk. A clean-looking new account tied to a referrer with dozens of prior referrals reads differently than the same account standing alone.
- Hold and challenge logic. Route high-risk relationships into a pending state instead of paying out immediately, and trigger step-up verification only for the risk bands that warrant it.
- Analyst review and feedback. Confirmed fraud and confirmed false positives both need to flow back into the rules engine or model training set, or the system stagnates.
Stripe's promo abuse guidance offers a concrete illustration: 15 accounts created from the same IP address within 48 hours merits investigation. Treat that as a starting point, not a fixed rule. A university campus or corporate NAT can produce similar volume from ordinary students or employees, so thresholds need tuning per campaign, vertical, and traffic source before they go live.
On the engineering side, persist relationship records in a dedicated table keyed by referral ID and device ID, not buried inside the user record. Emit events at click, signup, and each qualifying milestone, and wire the reward engine to check the current risk score before releasing any payout rather than defaulting to instant fulfillment.
Pro Tip: Observe new thresholds on real traffic before they affect payouts. Check false positives before using a cutoff to hold rewards, particularly in communities with shared networks or devices.
How Do You Read Device, Network, and Behavioral Signals?
No single signal proves referral fraud on its own. Interpretation matters more than collection.
- Device fingerprinting and risk signals. Persistent device recognition, including detection of VPNs, proxies, Tor exit nodes, and Apple Private Relay, lets you tie a "new" referee back to a device that already claimed three rewards this month. The limit: legitimate users on shared campus Wi-Fi or corporate VPNs will trip the same flags, so these risk signals work best as one input into a score, not a rejection trigger.
- IP and subnet velocity. A household sharing one IP across two or three signups looks nothing like a farm cycling through a /24 subnet to register dozens of accounts in an hour. Measure both count and time window, not count alone.
- Email signals. Disposable domains, systematic aliasing (
user+1@,user+2@), and email reuse across supposedly unrelated accounts are strong secondary indicators, particularly when paired with a device match. - Timing and redemption signals. Immediate reward redemption seconds after signup, or a batch of referrals completing within the same narrow window, points toward coordination rather than organic referral behavior.
Mastercard's loyalty fraud research makes the caution explicit: a shared IP, VPN, or device does not by itself justify an automatic rejection, since it can describe a household, a workplace, or a privacy-conscious customer just as easily as a fraud ring. The fix is risk banding: correlate weak signals, and reserve step-up verification for accounts that land in the Suspicious or Dangerous Risk Score band rather than issuing blanket challenges to everyone who trips one rule.
How Do You Detect Multi-Accounting in a Referral Program?
Start with the relationship between the referrer, the referred account, and the device behind each signup. A referral code appearing on three new accounts is ordinary if three different customers used it; three accounts linked to the same recognized visitor need a closer look. ShieldLabs detects Multi-accounting when three or more accounts are linked to one visitor, and reports the High-Risk Event at Medium or High confidence. That event is separate from the 0–100 Risk Score.
| What to compare | What it can show | What it cannot prove alone |
|---|---|---|
| Referrer and referee linked to the same visitor | A possible self-referral | Whether the accounts belong to one person in a shared household |
| Three or more accounts linked to one visitor | A Multi-accounting event worth reviewing | Whether every referral claim breached the program's terms |
| Reward claims, timing, and qualifying purchases | Whether linked accounts repeatedly claim value | Whether a shared device was used intentionally to exploit the program |
Keep the referral reward pending until its qualifying event, then review the linked accounts and the underlying risk signals before release. The program decides eligibility; ShieldLabs supplies the detection and evidence. If you are choosing between vendors, the multi-accounting detection tools comparison covers which products return a ready-made event and which require you to build the correlation yourself.
Should You Use Rules, Graph Analysis, or Machine Learning?
Legitimate referral networks branch. One satisfied customer refers three friends, who each refer one or two more, producing a loose tree with shallow, varied connections. Coordinated abuse tends to look like a star: one controlling identity sits at the center, radiating dozens of referral edges to accounts that share devices, IPs, or payment instruments. Stripe's guidance recommends analyzing clusters and edges directly instead of scoring each signup as an isolated event.
- Deterministic rules catch known abuse patterns cheaply and stay easy to explain to analysts and auditors.
- Machine learning and graph neural networks surface emergent, coordinated patterns that rules miss, but they need labeled data, ongoing monitoring, and retraining as fraud tactics shift.
- Combine both. An academic evaluation of a prompt-based fine-tuning approach for graph neural networks reported a significant improvement over two deployed voucher-abuse models in an online test, but that gain depended on clean labels and continuous validation.
Whichever method you pick, keep the underlying features explainable. An analyst clearing a flagged account needs to see why it scored high, not just the number.
Which Events Should Gate Reward Payout by Vertical?
Rewards should stay pending until a real qualifying event confirms the referral converted, and that event differs by industry.
- E-commerce: hold the reward until the referred order is fulfilled and the return window closes, or wait for a first paid order beyond any refund period.
- Fintech: tie release to a funded and cleared balance, completed KYC verification, or a finalized settlement event rather than account creation alone.
- Gaming: gate on a first real-money deposit, a gameplay or wagering threshold, or a short retention window that filters out accounts created purely to farm signup bonuses.
Extole's referral fraud guidance treats the moment between attribution and payout as the highest-leverage intervention point precisely because it is reversible. Default every reward to a pending state and automate the hold logic; reserve manual review for high-dollar-value claims where a wrong call carries real cost.
What Belongs on Your Implementation Checklist?
Before launch, confirm the data model and integration points can support the workflow above.
- Data model: persist referral ID, persistent visitor ID, device signals, IP history, payment events, timestamps, and outcome labels in one linked structure.
- Integration points: call detection logic at click, at signup, and again at the payment or activation event; run scoring server-side so the decision logic can't be bypassed client-side.
- Operational hooks: build a review queue for flagged relationships, capture analyst labels systematically, and feed confirmed outcomes back into your rules or model.
- Rate limits and idempotency: promo and referral endpoints need request throttling and idempotent handling, or a single script can hammer the same code hundreds of times in minutes.
ShieldLabs fits into this checklist as the detection layer: it identifies returning visitors with 99.9% identification accuracy even after cleared cookies or IP rotation, surfaces the signals behind each risk score for analyst review, and integrates through a JavaScript snippet or server-side SDK rather than a lengthy sales cycle.
Pro Tip: Log the risk score at the moment of the hold decision, not just at signup. Scores drift as new signals arrive, and you want an audit trail showing exactly what the system knew when it made the call.
How Do You Measure Referral Program Health?
Tracking fraud losses in isolation misses the other half of the picture: whether your controls are also suppressing genuine referrals. EY's loyalty fraud framework recommends tracking both sides together, and monitoring has to continue after signup since accounts can fail to convert or get reversed well after the fact.
| Metric | What it tells you |
|---|---|
| Fraud loss / avoided loss | Direct payout risk exposed or prevented from your own decisioning |
| Approved-referral conversion | Whether cleared referrals go on to become real customers |
| Reward cost per retained customer | True program ROI once fraud and churn are factored in |
| False-positive rate | How much genuine referral activity your rules are blocking |
| Review rate | Analyst workload and whether thresholds are too aggressive |
| Time to decision | How long referrers and referees wait for reward release |
Run cohort analysis comparing retention and revenue after immediate payout versus after a hold period, and watch for chargebacks or reversals that surface weeks later. Use every confirmed case, fraud or false positive, to retune thresholds and keep an audit trail for governance review.
Practical rollout advice

Immediate payout holds can create false positives before a team has measured its baseline. Start by observing scores and confirmed outcomes before changing the reward workflow. That gives you a baseline for how your thresholds actually behave against real traffic before you attach consequences to them.
Once you trust the scores, trial holds only on the Suspicious and Dangerous Risk Score bands, not the entire funnel. Label every confirmed case, fraud and false positive alike, since that labeled set is what eventually lets you move from static rules toward a model that adapts. And resist the urge to challenge everyone who trips a single signal. Step-up verification aimed at genuinely risky accounts protects conversion far better than blanket friction ever will.
Where ShieldLabs fits in a referral fraud workflow
ShieldLabs detects the identity layer of referral abuse: a returning device behind apparently new accounts. Each web identification includes a persistent Device ID with 99.9% identification accuracy, an explainable Risk Score and named risk signals from 300+ device and network signals. Multi-accounting is a ready-made High-Risk Event with Medium or High confidence, so a team can see linked accounts without building that detection from raw fingerprints.
The referral program still defines eligibility and payout timing. Feed ShieldLabs detections into that existing workflow to review suspicious claims before rewards are released. The Free plan includes 5,000 identifications, one time, without a card; Starter is $99 per month on monthly billing.
Sources
- How to detect promo abuse: a guide for businesses | Stripe
- Voucher Abuse Detection with Prompt-based Fine-tuning on Graph Neural Networks
- How do referral tools reduce fraud? A guide to detection and prevention | Extole
- Designed loyalty fraud whitepaper | EY
FAQ
What Is the Difference Between Referral Fraud and Loyalty Fraud?
Referral fraud targets the reward paid for bringing in a new customer, usually through fake or self-referred accounts. Loyalty fraud abuse points accounts, tiers, or redemption within an existing loyalty program, though both often rely on the same device and risk signals to detect.
How Do You Detect Referral Scams Without Hurting Conversion?
Use risk bands instead of blanket rules, reserving step-up verification for accounts that score Suspicious or Dangerous risk rather than challenging every new referral. Mastercard's research notes that a shared IP or device alone should never trigger automatic rejection, since it often describes ordinary households or workplaces.
What Signals Matter Most for Referral Program Security?
Device fingerprinting, IP and subnet velocity, email reuse patterns, and redemption timing each add diagnostic value, but none should stand alone. Stripe's guidance recommends linking referrer, referee, device, and payment data into one relationship record before scoring.
Does ShieldLabs Block Referral Fraud Automatically?
ShieldLabs links repeat devices and detects Multi-accounting as a High-Risk Event. A referral program can use that evidence in its existing review and payout workflow.
When Should a Referral Reward Actually Pay Out?
Hold the reward until a real qualifying event confirms the referral converted, such as a fulfilled order, a funded account, or a first deposit, rather than releasing it at signup. Extole's research treats the window between attribution and payout as the highest-leverage point to catch fraud before money moves.
Recommended
Related articles
Detect Free Trial Abuse with 300+ Signals for SaaS Teams
Detect free trial abuse without blocking real users. Use auditable signals, progressive friction, and metrics to protect conversion.

How to prevent bonus, promo, and coupon abuse: a detection playbook for developers
How to prevent bonus, promo, and coupon abuse: the mechanic behind it, the signals that flag an abused offer, and how to score a claim before you credit it.
Operators: Persistent IDs for Bonus Abuse Detection in 24–72 Hours
Capture deposit to withdraw events, prioritise persistent visitor IDs and cohort signals, and score bonus claims in real time to stop abuse.