The 8 best bonus and promo abuse prevention tools in 2026

Last updated on October 21, 2026 · 9 min read
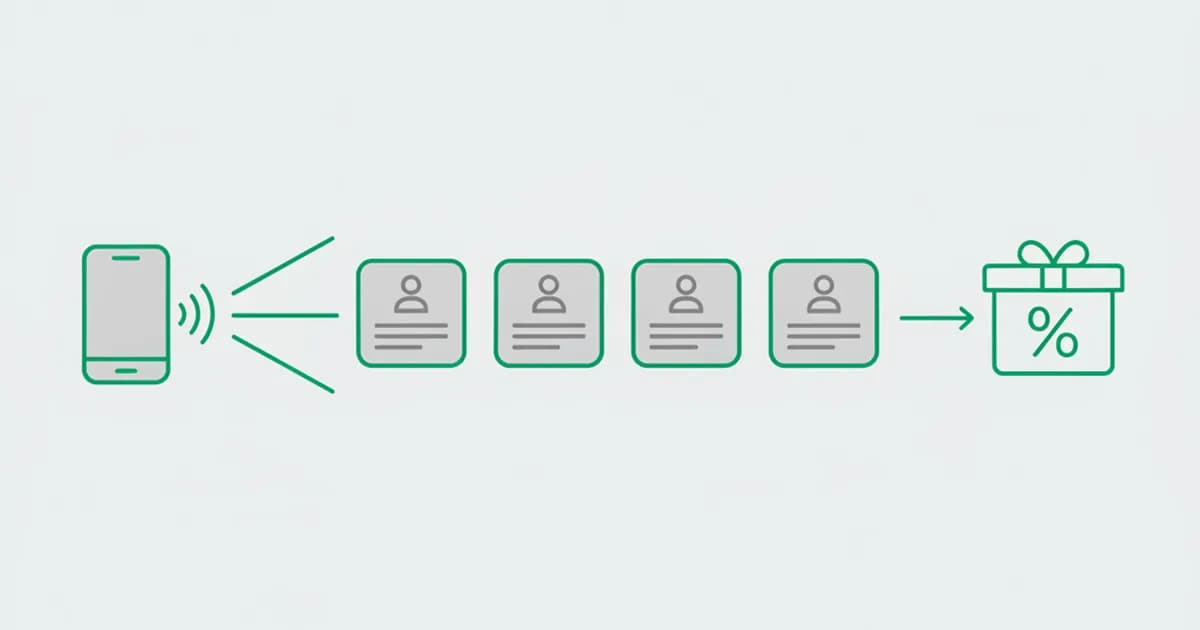
Bonus abuse prevention is the practice of stopping one person from claiming a promotion many times over by hiding behind many "new" accounts. The tactic is old and well documented: matched betting and bonus hunting turn welcome offers, deposit matches, and free bets into a repeatable payout, with organized communities and paid services built around it.
On iGaming platforms, rewards apps, and any product that pays new users to sign up, it shows up as the same person opening account after account, each dressed up to look like a first-time customer.
The mechanism underneath is almost always multi-accounting: one operator, many accounts, one payout repeated. It is a form of the Sybil attack described in 2002, where a single actor runs many fake identities to game a system, and it is the reason bonus abuse is treated as a first-class fraud category in defender resources like the Group-IB knowledge hub.
It is hard to catch because each account is built to look distinct, so the reliable way to unmask it is to find what the accounts share, most often the device and the network behind them.
This guide explains what bonus and promo abuse prevention is, how it works, and runs through the 8 best tools for 2026, grouped by how you buy and run them.
Key takeaways
- Bonus and promo abuse is one person claiming the same offer many times, and the mechanism behind it is almost always multi-accounting: many accounts, one real user.
- Simple per-account checks miss it because each signup looks new, so the signal that catches it is what the accounts share, usually a device or an anonymized network.
- The strongest prevention links bonus claims back to a persistent device identifier that survives cleared cookies and a rotated IP, then detects multi-accounting for the operator to act on.
- The market splits into platforms you can evaluate on your own traffic today and sales-led suites that bundle case management and compliance, such as identity verification and AML.
What is bonus and promo abuse prevention?
Bonus and promo abuse prevention is the practice of identifying when a single person is claiming a promotion repeatedly through multiple accounts, so the operator can hold or deny the extra claims.
It works by looking past the details a bonus hunter can freely change, name, email, phone, and payment method, to the things they cannot cheaply vary: the device they sign up from, the network they route through, and the way those accounts cluster together in time.
The core signal is a shared origin. When ten "different" accounts all claim the same welcome bonus from one machine, that is not ten new customers, it is offer abuse driven by one person.
Prevention tools differ in how durably they recognize the device behind the claims, how well they read anonymized connections built to hide it, and whether they detect multi-accounting for you or leave you to assemble it from raw signals.
How bonus and promo abuse prevention works
Good prevention reads several layers and correlates them into one picture:
- Device and identity linkage. A persistent device identifier links bonus claims back to one machine even after cleared cookies, a new browser profile, or a rotated IP. This is the single strongest signal, because the device outlives the disposable account details a bonus hunter resets between signups.
- Network and anonymity. Bonus hunters lean on VPNs, proxies, Tor, and anti-detect browsers to make one device look like a crowd of new customers from new places. A tool that names those risk signals can flag the evasion instead of being fooled by it.
- Shared attributes and velocity. Reused payment instruments, matching addresses, referral loops, and a burst of signups in a short window tie accounts together even when the device changes.
Tools that work combine these and, importantly, return ready-made detection rather than a pile of raw signals you have to correlate yourself. What separates them is the durability of the device signal, the depth of anonymity detection, and how much of the correlation is done for you.
A promo abuse campaign that pays out to many accounts run by one person is exactly the multi-accounting these tools are built to detect, so the operator can step in before the payout clears.
The tools below are grouped by how you buy and run them and listed alphabetically within each group.
Tools at a glance
This table summarizes the intended fit of each tool. The sections below explain its coverage and limits.
| Tool | Best fit |
|---|---|
| ShieldLabs | Teams that want multi-accounting detection ready-made, with named risk signals and an explainable score they can act on |
| Castle | Teams already on Cloudflare that want edge-plus-app coverage and are comfortable writing their own promo-abuse rules |
| IPQualityScore (IPQS) | Teams that mainly want IP, email, and phone reputation checks at promo signup and treat device linking as secondary |
| Arkose Labs | Large enterprises that want active, challenge-based mitigation against the automated mass signups behind large promo-farming attacks |
| SEON | IGaming and fintech operators that want enrichment, AML, and case management alongside device data, and can absorb an enterprise-style sales cycle |
| Sift | Larger operators that want promo and incentive-abuse coverage inside a broad, network-scale fraud platform and have the headcount to run it |
| Incognia | Mobile-first operators where user location adds a strong, hard-to-spoof signal for linking repeat promo claims across resets and reinstalls |
| Verisoul | Gaming and rewards teams that want an account-linking graph, with optional selfie verification available when proving one unique human matters |
Self-serve device and signal tools
These are platforms you can evaluate on your own traffic today: they start free or low, integrate without a sales call, and focus on surfacing the device and network signal behind repeat bonus claims. They fit any team that wants multi-accounting detected fast.
ShieldLabs
ShieldLabs is a platform built around the multi-accounting that drives bonus abuse, with enterprise-level functionality without enterprise pricing. You add one JavaScript snippet, and each visit returns persistent identification with 99.9% identification accuracy that survives cleared cookies and a rotated IP, so the many "new" accounts claiming one offer from a single device stay linked.
It automatically detects multi-accounting, account sharing, impossible travel, and account takeover. The risk score, bot and automation detection, and named risk signals, including VPN, proxy, Tor, and anti-detect browser use, show why the linked accounts warrant review.
ShieldLabs flags the abusive accounts and helps stop bonus abuse before the payout clears, so teams can decide whether to hold or deny each claim. Pricing is a one-time free allocation of 5,000 identifications, then plans from 99 USD a month.
ShieldLabs covers web traffic through one JavaScript snippet, with an API and webhooks on every plan.
Best for: teams that want multi-accounting detection ready-made, with named risk signals and an explainable score they can act on.
Castle
Castle is a self-serve account-security platform with a dual-layer architecture: it runs at the Cloudflare edge and inside your app through an SDK, so signals from one sharpen the other. Multi-accounting is an explicit use case, and its own example rule targets bonus abuse directly, counting unique users per device fingerprint where a promo code exists over a time window.
It returns three scores from 0 to 100 for bot, abuse, and account takeover, backs them with device fingerprinting it rates up to 99.5 percent accurate, and gives you a customer-owned rules engine. Pricing starts free at 1,000 calls a month, then Pro at 200 USD a month.
The tradeoff is that Castle gives you the building blocks, not a finished pattern. Promo abuse is a rule you compose and tune rather than a named detection surfaced for you, the scoring leans on self-learning models, and its public review base is thin.
Best for: teams already on Cloudflare that want edge-plus-app coverage and are comfortable writing their own promo-abuse rules.
IPQualityScore (IPQS)
IPQualityScore pairs IP reputation with email and phone validation to flag bonus signups that route through a suspicious connection or reuse a burned contact detail. Its VPN, proxy, Tor, and residential-proxy detection is backed by a proprietary honeypot network across many countries, and it ships dedicated affiliate-fraud and duplicate-account detection features that map onto promo abuse.
Free interactive lookup tools make it easy to test before committing. A permanent free tier covers 1,000 lookups a month, with self-serve plans from 99 USD a month.
The tradeoff sits in the packaging. On the self-serve tiers you get IP, email, phone, and URL reputation, but device fingerprinting and the mobile SDK are gated to a custom Enterprise plan, so the device-linkage layer that catches multi-accounting is not in the entry tiers.
Output is a score from 0 to 100 plus raw signals, and reviewers flag a dated dashboard, so you assemble the bonus-pattern yourself.
Best for: teams that mainly want IP, email, and phone reputation checks at promo signup and treat device linking as secondary.
Enterprise fraud platforms
These are sales-led suites that bundle case management and compliance, wrapping the abuse signal in identity verification, AML, or active challenges. They fit regulated operations with a staffed fraud team.
Arkose Labs
Arkose Labs is an enterprise platform built around challenge-based mitigation, and its Attack Economics model aims to make mass abuse economically unviable rather than merely block it.
On suspect traffic it deploys an adaptive Matchkey challenge that is cheap for a human but expensive for automation, which raises the cost of spinning up the flood of accounts a large promo-farming operation depends on.
Fake account creation, spam and abuse, and account enumeration all sit in its solutions catalog, backed by a cross-customer intelligence network and a 24/7 managed SOC.
The tradeoff is friction, fit, and access. Arkose leads with active challenges, so real users can meet a puzzle, and its model centers on automated traffic rather than a passive multi-accounting signal layer. Pricing is enterprise-only and opaque, sits in the top cost bracket, and setup runs to multiple weeks.
Best for: large enterprises that want active, challenge-based mitigation against the automated mass signups behind large promo-farming attacks.
SEON
SEON is a fraud platform widely used in iGaming and fintech, and bonus abuse is one of its named use cases. It pairs device intelligence with data enrichment: it resolves an email or phone number into a wider digital footprint and links accounts that share otherwise hidden attributes, which is how it surfaces the same person behind many bonus claims.
It markets 900-plus signals, transparent and explainable scoring, a custom rules engine, case management, and AML tooling, so a fraud team can move from a flagged multi-accounting cluster to an investigation in one console. The Starter tier is published at 699 USD a month for 2,500 fraud checks, with everything above that quoted by sales.
The tradeoff is cost and access at the small end. That entry price works out to roughly 28 cents per check, and past a few thousand checks a month you move into a sales-quoted plan, with a "speak with an expert" call rather than an instant signup. Reviewers also note a learning curve and ongoing rule calibration.
Best for: iGaming and fintech operators that want enrichment, AML, and case management alongside device data, and can absorb an enterprise-style sales cycle.
Sift
Sift is an enterprise fraud platform that added a specialized console module for incentive abuse in 2025, covering loyalty fraud, promo exploitation, and referral abuse. It scores signups and actions against a large cross-network dataset, reportedly around a trillion events a year from tens of thousands of sites, to flag coordinated multi-account activity claiming the same offer.
The Sift Score is delivered through an analyst console and an embeddable API, backed by a cross-network scoring engine and, on contract, a team of trust-and-safety specialists, and it serves hundreds of brands across commerce, marketplaces, fintech, and gaming.
The tradeoff is cost and opacity. There is no public pricing, no free tier, and no self-serve signup; you buy an annual enterprise contract, and implementation averages around two months.
Reviewers describe the model as a black box that is hard to second-guess, and note that many signals firing at once can bury the one that matters, so it rewards a staffed fraud team over a small one.
Best for: larger operators that want promo and incentive-abuse coverage inside a broad, network-scale fraud platform and have the headcount to run it.
Mobile and account-linking specialists
These tools bring a signal the web-and-signal tools do not: reinstall-proof mobile identity plus location, or a real-time graph of which accounts share a device. They fit native apps and teams that want the link drawn for them.
Incognia
Incognia is a device and location intelligence platform delivered mainly as a mobile SDK, and it lists promo and refund abuse among its core use cases in food delivery and ride-share.
It links accounts through a reinstall-proof device identifier plus proprietary location signals from GPS, Wi-Fi, Bluetooth, and cellular triangulation, so it can tie repeated promo claims to one real user and one real place even across resets and reinstalls.
That location layer catches things pure device tools miss, and it maintains dedicated iGaming and casino fraud pages for the gambling vertical.
The tradeoff is surface and access. Incognia is mobile-SDK-first, its browser identifier only launched in 2026, and the whole customer base is app-centric, so it fits native apps far better than a web signup flow. Pricing is enterprise-only and volume-based, with no published tiers and every path routing to a demo rather than a self-serve trial.
Best for: mobile-first operators where user location adds a strong, hard-to-spoof signal for linking repeat promo claims across resets and reinstalls.
Verisoul
Verisoul is a fake-account prevention platform with a customer footprint in gaming and rewards, where bonus and promo abuse concentrate. Its Account Linking graph visualizes in real time which accounts share a device or fingerprint, which is the direct view an operator needs to spot one person farming a promotion across many signups.
It combines device fingerprinting, proxy and VPN detection, and optional selfie and document verification through FaceMatch and ID Check, and it offers a no-code rule builder so decisions can be tuned without engineering. Paid plans start at 249 USD a month for the Professional tier.
The tradeoff is access and identifier model. The free Starter tier is dashboard-only with no API, and every self-serve button routes to a demo, so there is no instant signup. Verisoul also returns match probabilities rather than a stable device identifier you can join in your own warehouse.
Best for: gaming and rewards teams that want an account-linking graph, with optional selfie verification available when proving one unique human matters.
How to choose
No single tool on this list is the universal answer, and many operators end up layering two: a device and signal layer for the everyday case, and a broader platform or verification step for organized rings. Start from your own threat model and how much you want done for you.
Three questions decide most of it. First, do you want the multi-accounting behind bonus abuse detected for you out of the box, or the raw signals to build your own rules on?
A tool with ready-made multi-accounting detection saves your team from writing correlation logic; one that returns a device identifier or a set of signals expects you to build the linking rules yourself. Second, is your surface web or mobile?
A JavaScript-first tool and a mobile-SDK-first tool are genuinely different fits, and a sportsbook web platform has different needs than a native rewards app. Third, do you also need identity verification, payments, AML, or case management around the abuse signal?
If yes, an enterprise fraud suite earns its cost; if you only need multi-accounting detected fast, a platform you can evaluate on your own traffic today covers it quickly.
Match those answers to the entries above. If your problem is everyday welcome-bonus, deposit-match, or promo-code farming on the web, a device-intelligence platform you can test on your own traffic covers most of it in an afternoon. If you run a regulated iGaming operation that needs AML and case management, a platform like SEON or Sift earns its cost.
If your product lives in a native mobile app, a location- or SDK-first vendor may link claims your web stack cannot.
Sources
- Wikipedia: Matched betting
- Wikipedia: Sybil attack
- Wikipedia: Sock puppet account
- Group-IB: Knowledge Hub
Recommended
Frequently asked questions
- What is bonus and promo abuse?
- Bonus and promo abuse is one person claiming a promotion many times over, usually by opening multiple accounts that each look like a first-time customer. It covers welcome bonuses, deposit matches, free bets, referral rewards, and promo codes, and it is most common in iGaming, rewards apps, and any product that pays new users to sign up.
- Is bonus abuse illegal?
- Usually not by itself. Claiming the same bonus through multiple accounts is normally a breach of a platform's terms of service rather than a crime, and practices like matched betting are legal but still violate most bookmaker terms. It crosses into illegal territory when it involves genuine fraud, such as stolen payment cards, synthetic or stolen identities, or money laundering.
- How do you detect bonus and promo abuse?
- By finding what the accounts share rather than what they show. The strongest signal is a shared device, linked with a persistent device identifier that survives cleared cookies and rotated IPs, followed by network and risk signals like VPN, proxy, and anti-detect browser use, and shared attributes such as reused payment methods or a burst of signups in a short window.
- What is the best bonus abuse prevention tool for a small team?
- A device-intelligence platform you can evaluate on your own traffic, with a free tier, is usually the right starting point, because it can be integrated and tested without a sales process and catches the most common case, many bonus claims from one device.
- How does ShieldLabs help prevent bonus abuse?
- ShieldLabs detects multi-accounting, account sharing, impossible travel, and account takeover automatically, linking bonus claims back through persistent identification with 99.9% identification accuracy that survives cleared cookies and a rotated IP, alongside named risk signals, bot and automation detection, and a risk score from 0 to 100. It flags the abusive accounts with the evidence and helps stop bonus abuse, so teams can decide whether to hold or deny each claim.
- Which platforms detect users creating multiple accounts to abuse promotions?
- Evaluate platforms that connect registrations by device and account evidence, then associate those links with offer claims and redemptions. Require an explanation of each link and a review path for legitimate shared devices. Confirm that eligibility and redemption checks use the actual promotion terms rather than assuming every linked account is ineligible.
Related articles
The 8 best free-trial abuse prevention tools in 2026
The 8 best free-trial abuse prevention tools in 2026, how prevention works by linking many trial signups back to one device, and how to choose.

How to prevent bonus abuse in iGaming without an ID gate
How to prevent bonus abuse in iGaming: the signals that reveal one person behind many accounts, how casinos spot multiple accounts, and how to stop it.

Account and offer abuse in ecommerce: a merchant's playbook
The account and offer abuse an ecommerce store faces, why it is not payment fraud, and how to read the device behind each signup without blocking shoppers.
