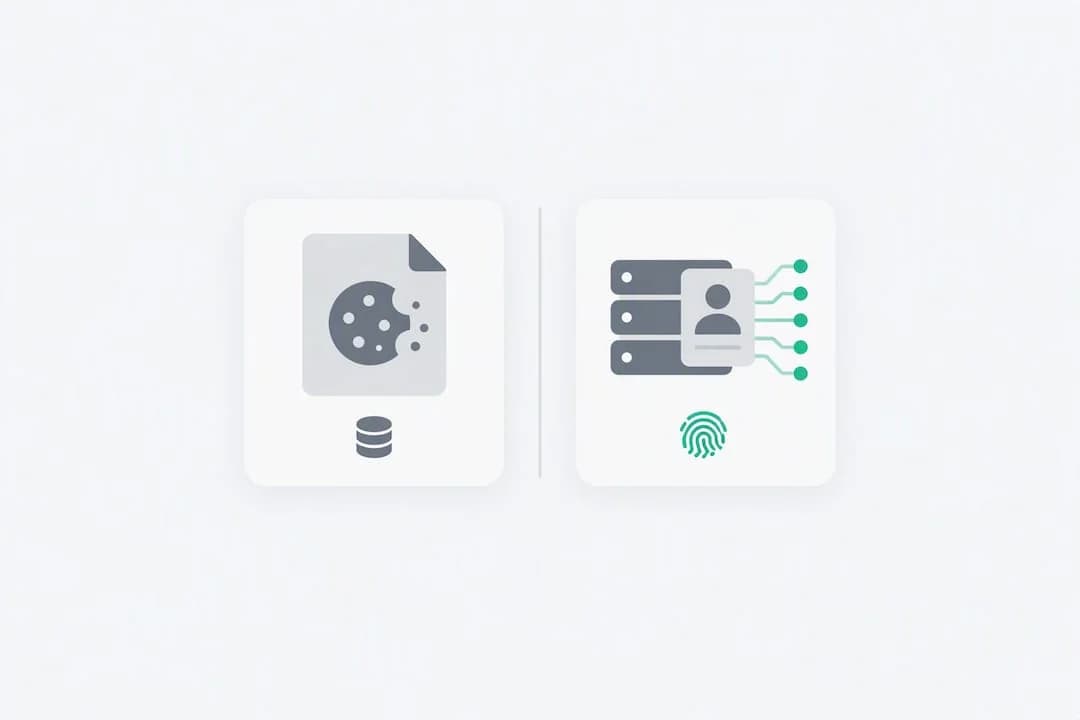
Fingerprinting vs Cookies: Key Differences for Fraud Teams
How cookies differ from server-side fingerprinting, why many cookieless claims mislead, and practical steps for developers and fraud teams.
Blog / Fraud prevention
How cookies differ from server-side fingerprinting, why many cookieless claims mislead, and practical steps for developers and fraud teams.
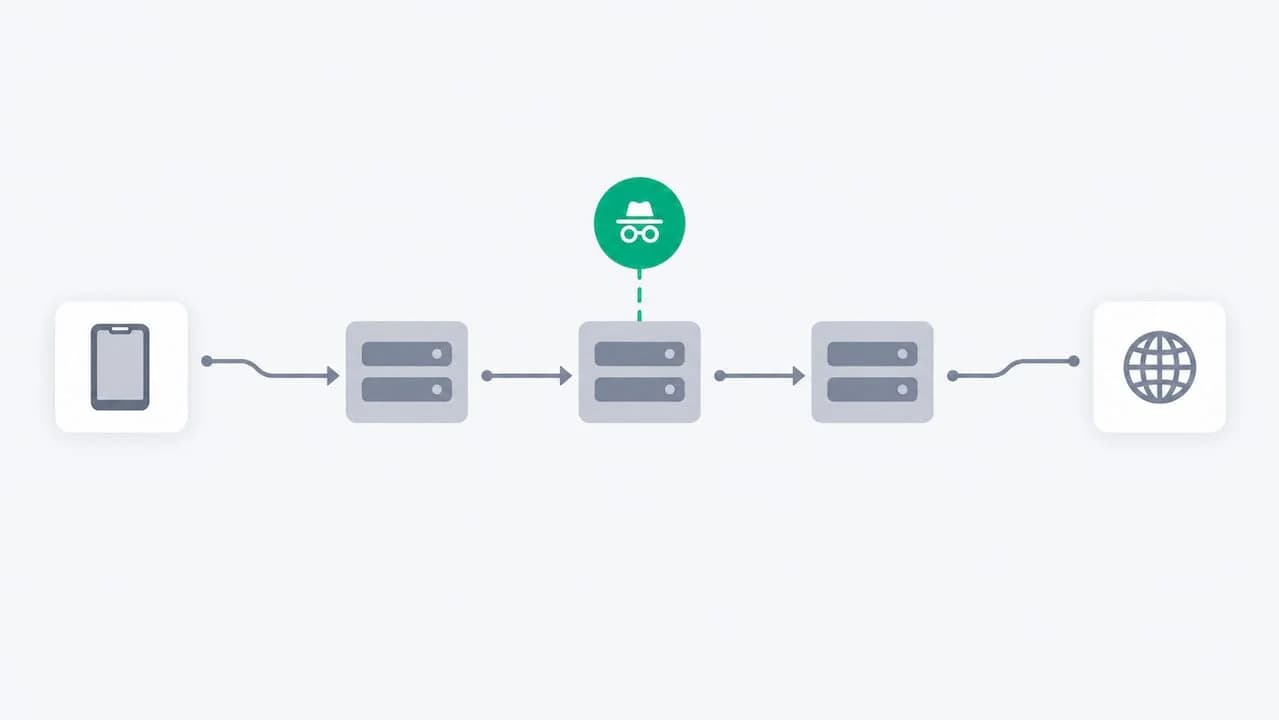
Ops guide to detecting Apple Private Relay. Learn three detection techniques, when to return NXDOMAIN, and fraud safe rules for teams.
Research backed playbook for fraud teams: five low latency checks to spot anti detect browsers, signal to score mapping, and a ShieldLabs setup path.
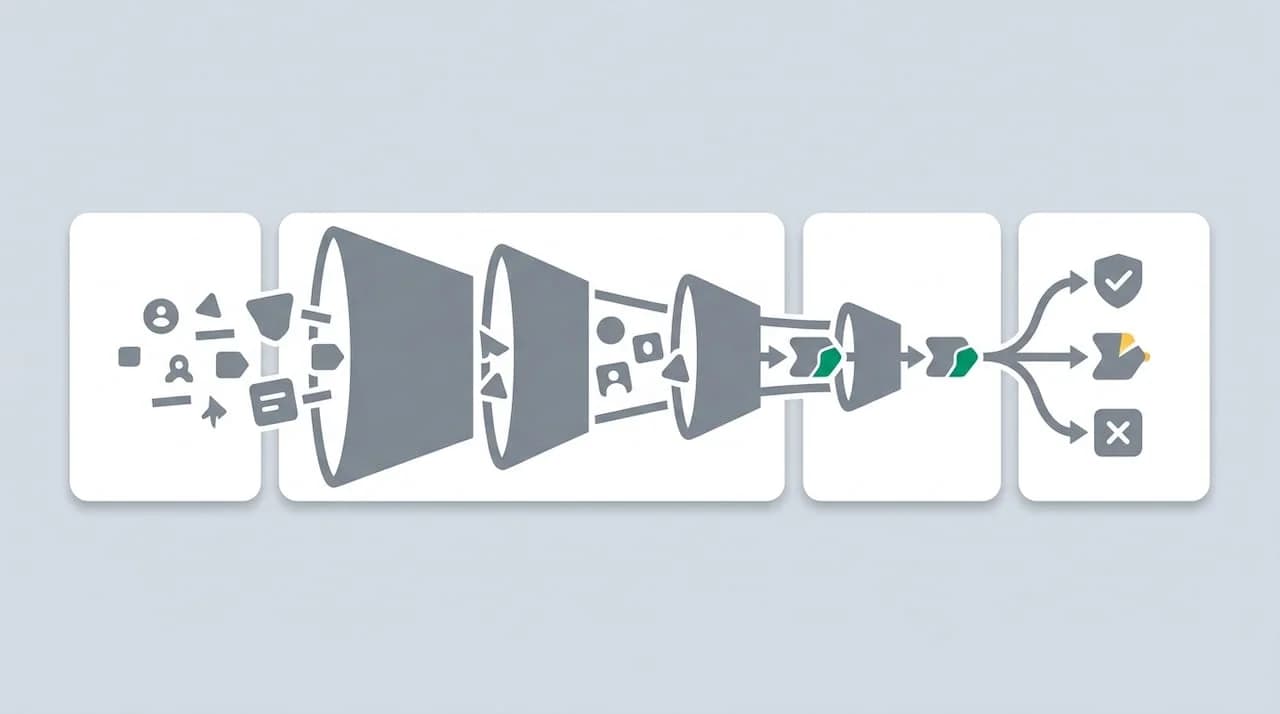
Practitioner guide to fake signup detection: build a four stage risk funnel and use persistent visitor IDs and auditable signals to cut fake accounts.
Playbook for fraud teams: measure rule-level false positives, run shadow tests and regression checks, then add visitor ID signals to cut noise.
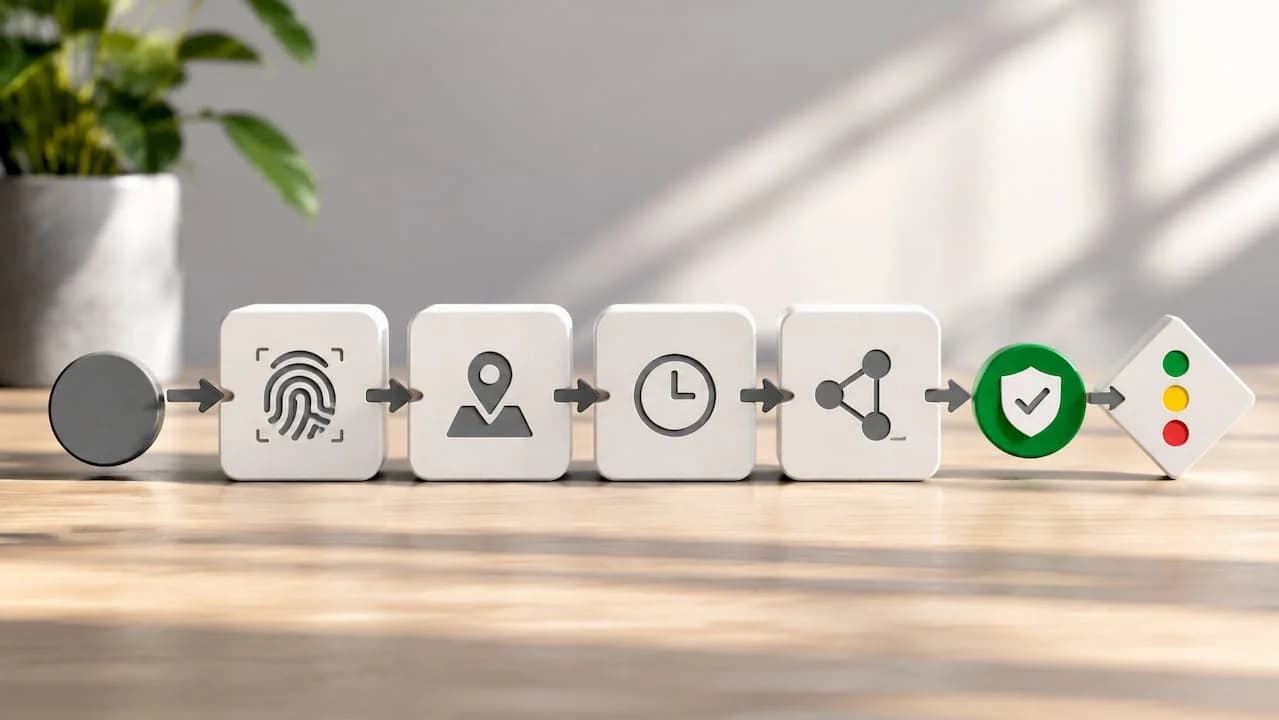
Integration-ready guide for engineering teams adding passive signals to a risk-based auth stack: the four-stage flow and sub-100ms latency targets.
Guest checkout removes the account history that flags a repeat fraudster. See how the device behind accountless orders restores that continuity.
What ticket scalping is, how scalpers beat per-person limits with fake accounts, and how the device behind those accounts links them back to one buyer.
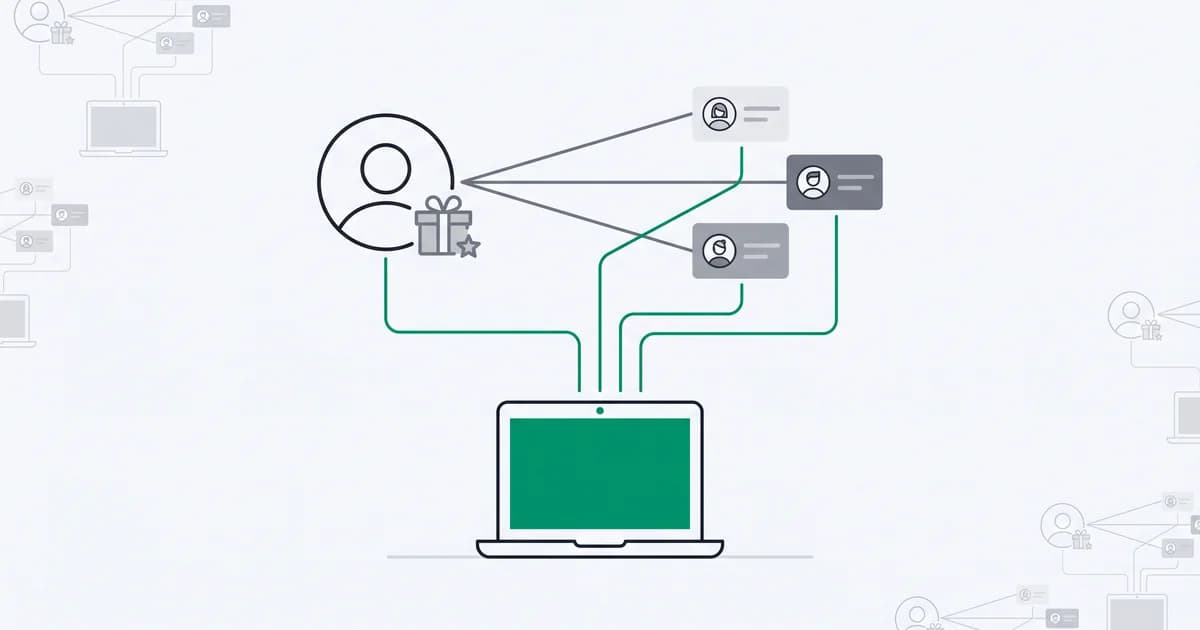
What referral fraud is, the main types from self-referral to account farming, why it is hard to catch, and how the device behind fake referrals stops it.
What loyalty fraud is, the main types from points theft to fake-account farming, why rewards programs are targets, and how device signals help stop it.
The merchant side of gift card fraud: how fraudsters cash out stolen cards, farm gift-card promos, and how the device behind those accounts links them.
What BNPL fraud is, the main types from account takeover to loan stacking, why the model is so exposed, and how to prevent it with device-level signals.


