How to prevent affiliate fraud
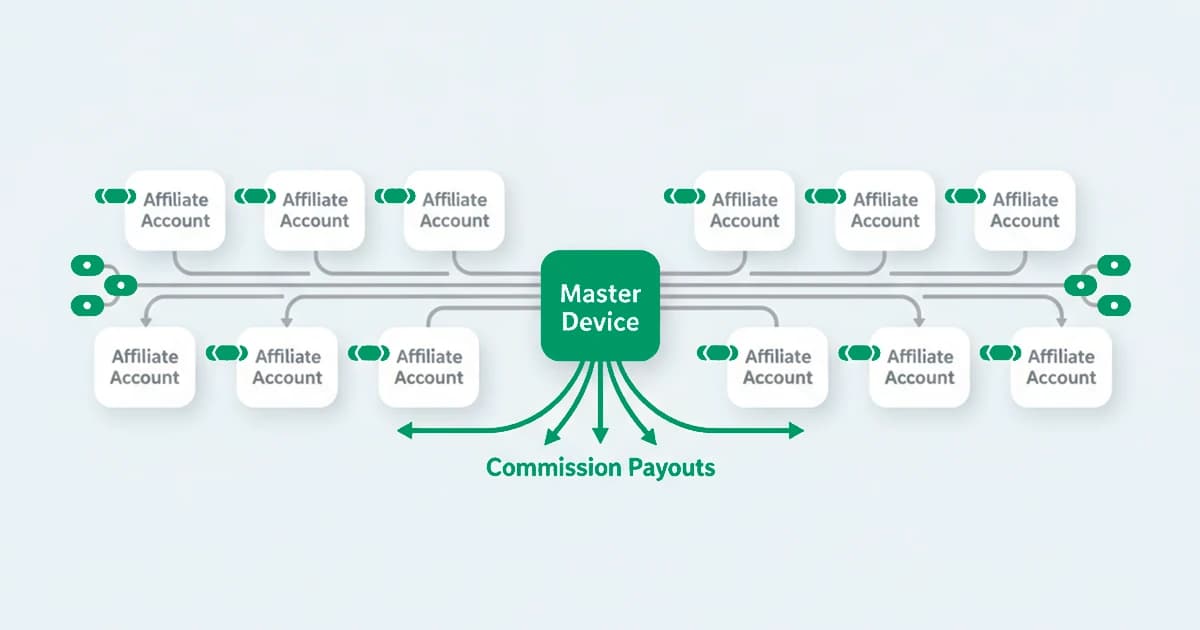
What affiliate fraud is, its main types from cookie stuffing to fake leads and self-purchases, and how the device behind a fake conversion gives the ring away.
Kanstantsin Serabrakou is the Chief Technology Officer at ShieldLabs, where he leads engineering and the device-intelligence and detection systems behind the product.
What affiliate fraud is, its main types from cookie stuffing to fake leads and self-purchases, and how the device behind a fake conversion gives the ring away.
The 10 best multi-accounting detection tools in 2026, how detection works by linking accounts to a shared device and network, and how to choose.
The 14 best account takeover detection tools in 2026, how ATO detection works, and how to choose across device, behavioral, identity, and bot defenses.
What synthetic identity fraud is, how the fabricated-identity lifecycle works, why it is so hard to detect, and how device signals expose the ring behind it.
Compare 10 fraud prevention and detection tools for device intelligence, account abuse, payment risk, and chargebacks. Features, fit, and pricing models.
What an IP fraud score means, how Talos, Scamalytics, and IPQS calculate it, why yours can be high through no fault of your own, and what a score misses.
How to detect geolocation spoofing: how it works, why a single IP check fails, and how layered signals expose the mismatch so your team can prevent fraud.
What cookieless device identification is, how it recognizes a returning device without a stored cookie, and why it is not the same as cookieless analytics.
What iCloud Private Relay and Chrome IP Protection actually change for fraud detection: what degrades, what survives, and why masking is not evasion.
Friendly fraud is when a real customer disputes a purchase they made. How it works, why it is hard to prove, and how device evidence helps you fight it.
TLS fingerprinting identifies the software behind a connection from its TLS handshake. How it works, what JA3 and JA4 are, and what it reveals.
How to detect account takeover at login: the device and network signals that flag a suspicious login, why MFA alone misses them, and where the gap is.
